Description
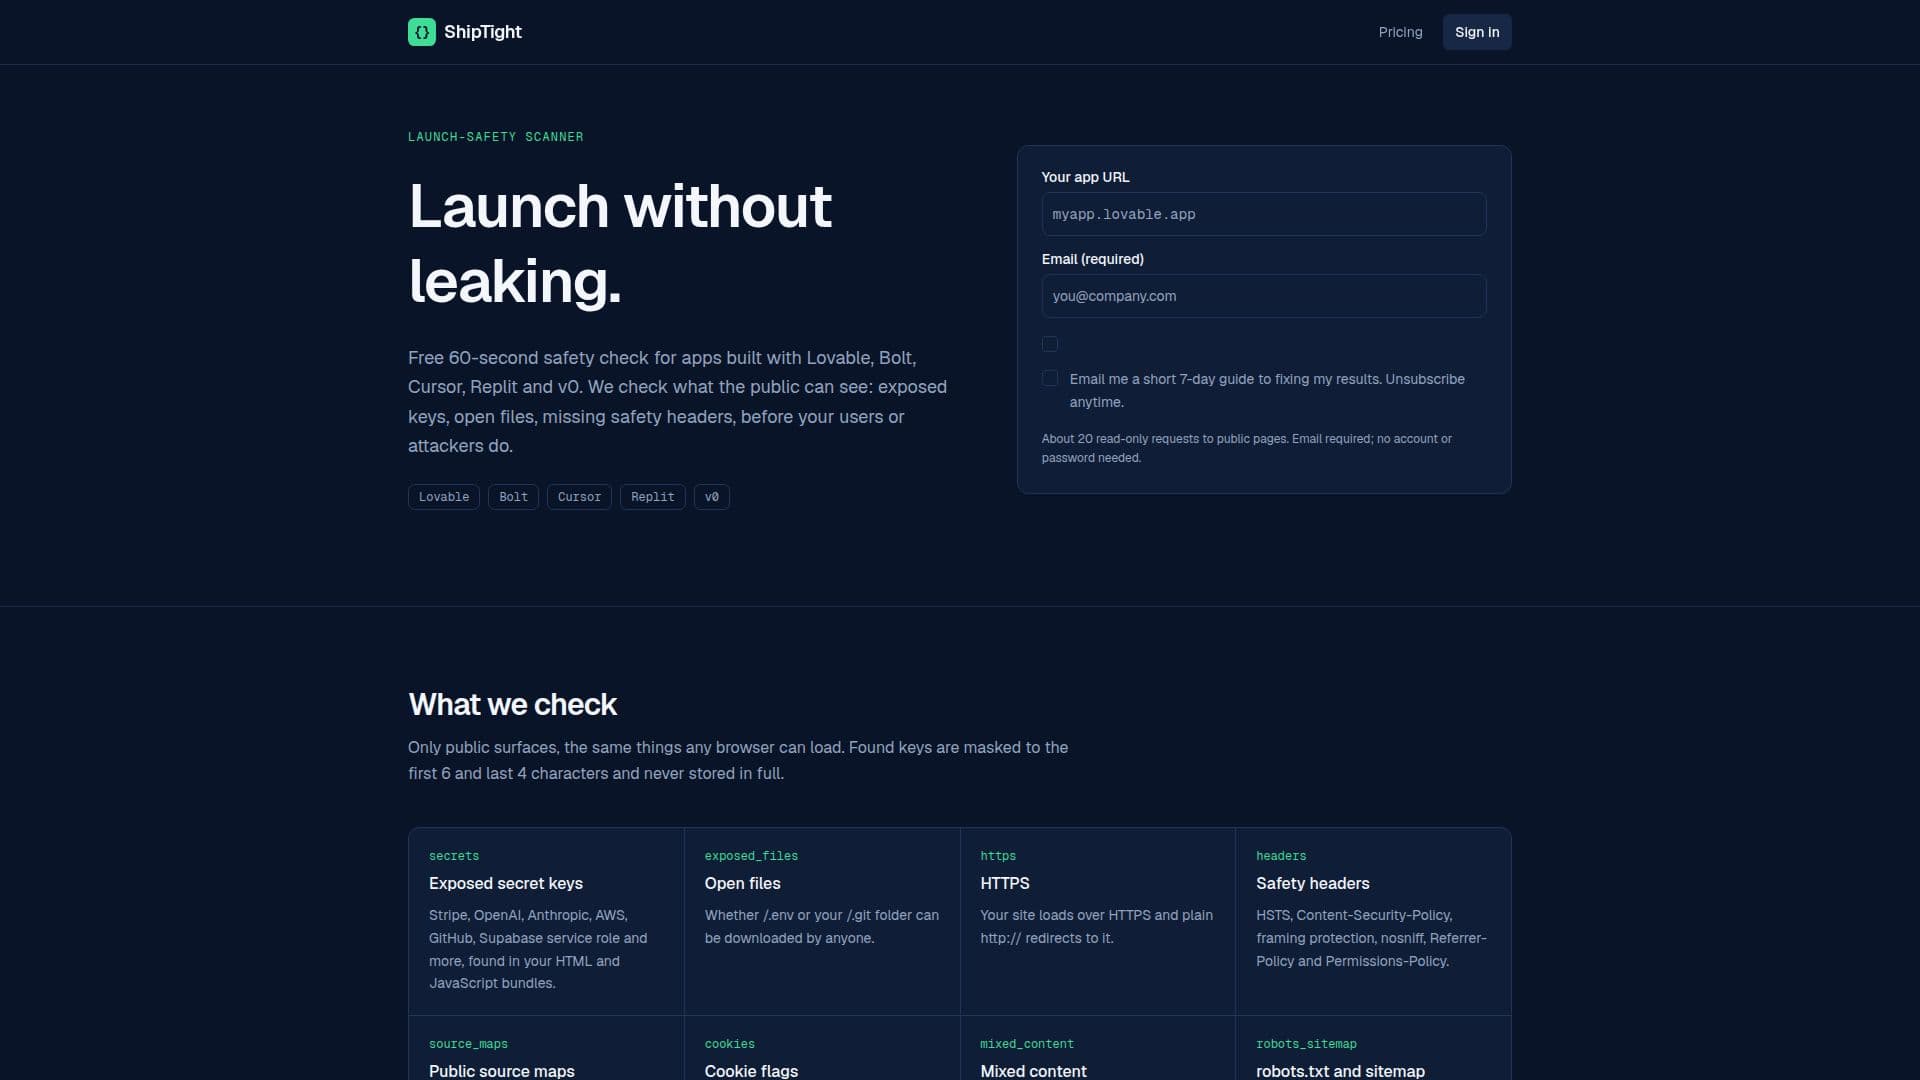
ShipTight provides a crucial launch-safety scan designed specifically for applications developed using modern AI builders such as Lovable, Bolt, Cursor, Replit, and v0. The service performs a rapid, 60-second check to identify common security vulnerabilities that could expose sensitive information or compromise an application's integrity.
Read More
The scanner focuses exclusively on public-facing surfaces, mimicking what any browser or potential attacker can see. It meticulously checks for exposed secret keys (e.g., Stripe, OpenAI, Anthropic, AWS, GitHub, Supabase service roles) found within HTML and JavaScript bundles. To ensure privacy, any discovered keys are masked, showing only the first six and last four characters, and are never stored in full. ShipTight also verifies for publicly accessible files like `.env` or `.git` folders, which could inadvertently expose configuration or source code.
Beyond file exposure, the service assesses critical safety headers, including HSTS, Content-Security-Policy, framing protection, nosniff, Referrer-Policy, and Permissions-Policy, ensuring robust browser security. It checks for proper HTTPS implementation, confirming that sites load securely and redirect from HTTP. Public source maps are also scrutinized to prevent original source code from being rebuilt. Additionally, ShipTight identifies insecure cookie flags (missing Secure, HttpOnly, or SameSite attributes) and mixed content issues where HTTP resources are loaded on an HTTPS page. It also verifies the presence and correct configuration of `robots.txt` and `sitemap` files, ensuring sensitive paths are not inadvertently exposed.
ShipTight streamlines the remediation process by detecting the specific builder used (Lovable, Bolt, Replit, v0, or Cursor), allowing it to generate tailored fix prompts. Users simply paste their app's URL and email, receive a safety score (0-100) and grade with top findings in about a minute, and then copy ready-to-paste fix prompts into their builder. A one-click re-check confirms the fixes. The service offers a free scan for basic findings, a one-time Full Fix Report for $49, and ongoing monitoring plans starting at $29/month, with an optional Revenue Guard add-on for payment failure alerts. ShipTight is operated by Game Gifted Entertainment LLC and emphasizes user privacy, storing only necessary data and never selling it.
- CategoryAI Cybersecurity Tools
- Pricing ModelFreemium
- DeploymentCloud
- PlatformsWeb
ShipTight's Core Features
60-second launch-safety scan
Checks for exposed secret keys (Stripe, OpenAI, AWS, GitHub, etc.)
Identifies publicly accessible files (.env, .git folders)
Verifies HTTPS implementation and redirects
Scans for missing or misconfigured safety headers (HSTS, CSP, etc.)
Detects public source maps that could expose original code
Checks for insecure cookie flags (Secure, HttpOnly, SameSite)
Identifies mixed content issues on HTTPS pages
Verifies robots.txt and sitemap presence and configuration
Detects app builder (Lovable, Bolt, Cursor, Replit, v0) for tailored fixes
Provides a 0-100 safety score and grade
Generates plain English findings and fix prompts
Offers one-click re-check after applying fixes
Provides one-time reports or ongoing monitoring
Includes optional Revenue Guard for payment alerts
How to use ShipTight?
Paste URL: Add your live app address and email to start a scan.
Get Score: Receive a 0 to 100 safety score, grade, and top findings in about a minute.
Copy Fix Prompt: Get ready-to-paste fix prompts tailored to your builder (Lovable, Bolt, Cursor).
Re-check: Apply the fixes and re-check with one click to confirm resolution.
Monitor (Optional): Subscribe for weekly re-scans, full reports, and dashboard history.
ShipTight's Use Cases
- Pre-Launch Security Audit
- Exposed Key Detection
- Public File Exposure Check
- Safety Header Validation
- HTTPS Configuration Review
- Source Code Leak Prevention
- Insecure Cookie Flag Identification
- Mixed Content Resolution
- Ongoing Security Monitoring
- Payment System Health Check