Description
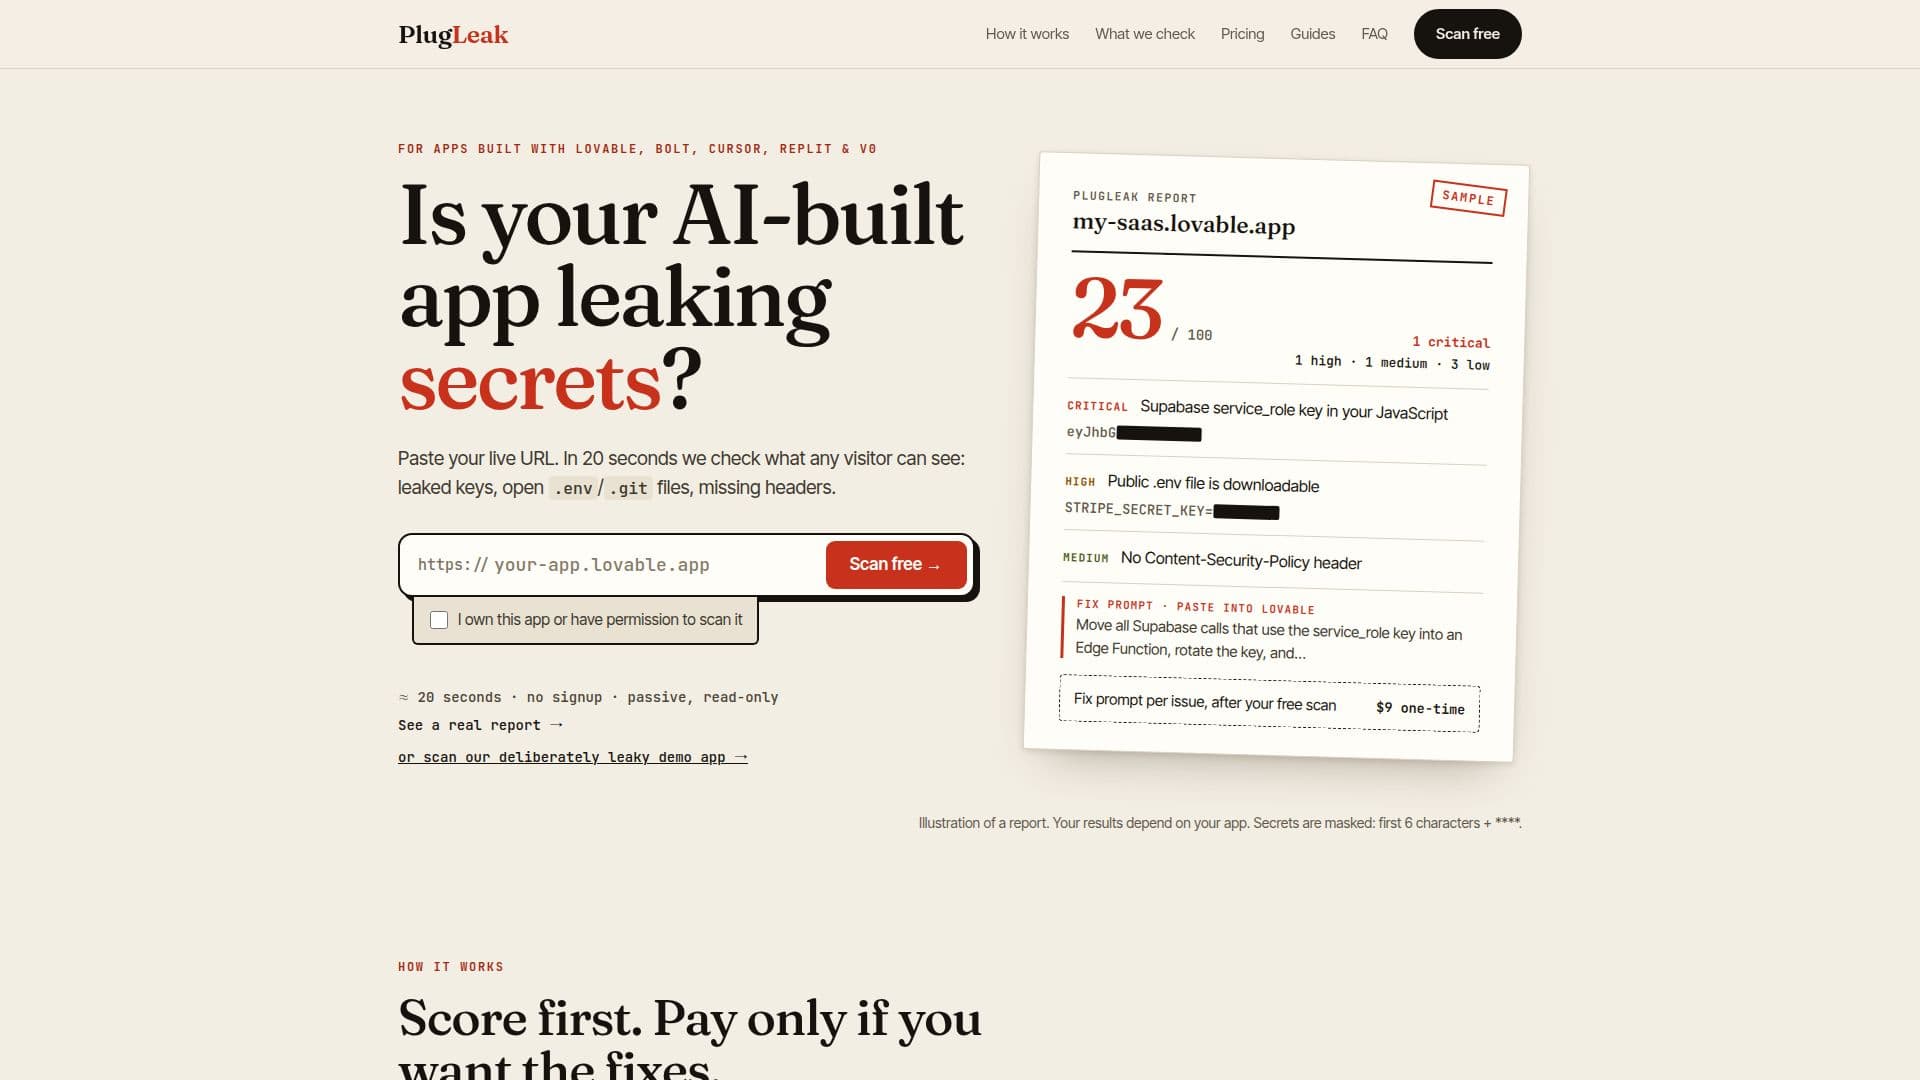
PlugLeak provides a specialized security scanning service designed for applications built using AI development platforms such as Lovable, Bolt, Cursor, Replit, and v0. The core offering is a rapid, free 20-second scan that performs a passive, outside-in check of a live application's publicly exposed elements. This process mimics the GET requests a standard visitor's browser would make, plus specific requests to /.env and /.git/config, without logging in, submitting forms, or querying databases.
Read More
The scanner meticulously searches for critical vulnerabilities, including leaked API keys (Stripe, OpenAI, Anthropic, AWS, GitHub, Supabase), exposed Supabase `service_role` keys, publicly accessible `.env` and `.git` configuration files, and missing essential security headers like Content-Security-Policy, Strict-Transport-Security, and X-Frame-Options. It also verifies HTTPS redirection and SSL certificate validity. Any secrets discovered are masked immediately (first 6 characters + ****) before being saved in the report, ensuring full keys are never stored.
Upon completion, users receive a security score out of 100. Providing an email unlocks a comprehensive problem list detailing each finding, its location, and masked evidence. For those seeking immediate remediation, PlugLeak offers paid "Fix Reports." A one-time payment of $9 provides copy-paste fix prompts tailored for Lovable, Bolt, or Cursor, guiding developers on what to rotate and how to verify the fix. A $29 option includes 10 fix reports, allowing for re-scans after deployments.
PlugLeak emphasizes its safety for live production applications, stating it only performs passive checks and never attempts exploits. It is not a full security audit but rather an automated check for common, costly mistakes that can lead to data breaches. The service is ideal for developers and teams using AI builders who need a quick, reliable way to identify and address public-facing security flaws before they are exploited.
- CategoryAI Cybersecurity Tools
- Pricing ModelFreemium
- DeploymentCloud
- PlatformsWeb
PlugLeak's Core Features
Free 20-second security scan for live apps
Detects leaked API keys (Stripe, OpenAI, Anthropic, AWS, GitHub, Supabase)
Identifies exposed Supabase service_role keys
Checks for publicly accessible .env and .git files
Scans for missing security headers (CSP, HSTS, X-Frame-Options, etc.)
Verifies HTTPS redirection and SSL certificate validity
Provides a security score out of 100
Offers detailed problem lists with masked evidence (after email submission)
Includes copy-paste fix prompts for Lovable, Bolt, and Cursor apps (paid feature)
Supports re-scans after deployments with credit packs
Passive scanning method, safe for production environments
Does not log in, submit forms, or query databases during free scan
Masks all discovered secrets before storage
Offers free guides for self-remediation
Identifies requests with "PlugLeakScanner" User-Agent in logs
How to use PlugLeak?
Paste URL: Enter the live URL of your AI-built application.
Initiate Scan: Confirm ownership or permission to scan the application.
Get Score: Receive an immediate security score out of 100.
View Problems: Enter your email to unlock the full list of identified security problems and masked evidence.
Access Fixes (Optional): Purchase a Fix Report for copy-paste prompts tailored to Lovable, Bolt, or Cursor to resolve issues.
Verify Fixes: Use the provided guidance to rotate keys and verify that vulnerabilities have been addressed.
PlugLeak's Use Cases
- Pre-deployment Security Check
- Post-deployment Vulnerability Assessment
- Developer Security Education
- Compliance and Risk Mitigation
- Rapid Security Feedback
- AI Builder Security Hardening