Description
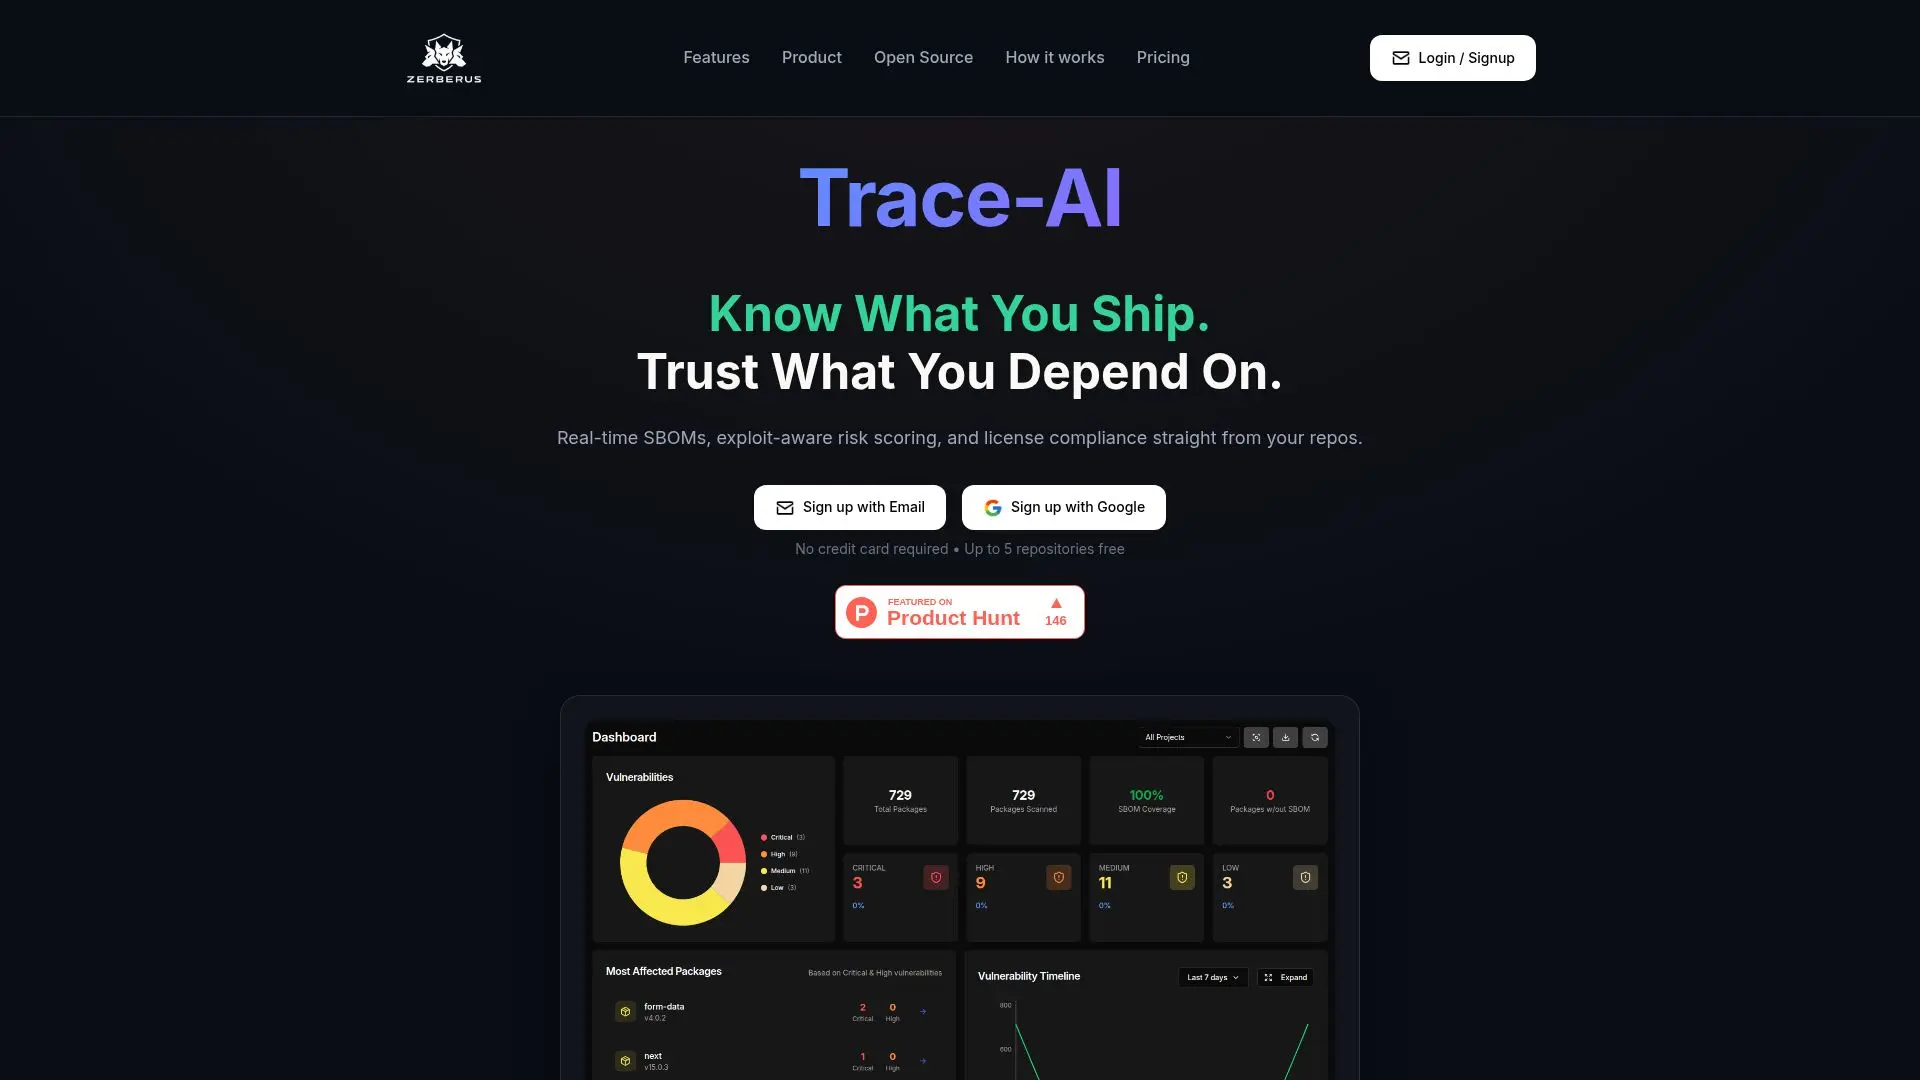
Trace-AI, by Zerberus, is a software supply-chain security tool that helps you know what you ship and trust what you depend on. It connects to your GitHub or GitLab repositories and generates real-time Software Bills of Materials (SBOMs) in CycloneDX and SPDX formats, tracking direct and transitive dependencies continuously as your code evolves.
Read More
Beyond generating SBOMs, Trace-AI moves past raw CVE dumps with exploit-aware scanning that prioritizes vulnerabilities that are actually exploitable, so you fix the real risks first with full context. It identifies copyleft licenses like GPL and LGPL instantly to avoid surprises during enterprise review, and tracks vendors alongside code dependencies including APIs, SDKs, SLA expiry, and breach history. A dashboard shows critical, high, medium, and low exposure in one place, and every package, CVE, and version is visible without a black box. It maps SBOM data to compliance frameworks such as ISO 27001, SOC 2, PCI-DSS, HIPAA, and GDPR, and exports audit-ready evidence as CycloneDX, SPDX, or JSON.
Trace-AI emphasizes open-source transparency: its underlying ZSBOM classification logic is public and auditable, policy checks are published as forkable YAML or JSON, and risk scoring, license mapping, and vendor thresholds are editable. It analyzes only dependency manifests and lock files, never your source code, and can be run locally. The first 5 repositories are free with no credit card required.
- CategoryAI Cybersecurity Tools
- Pricing ModelFreemium
- DeploymentCloud, Self-hosted
- PlatformsWeb
Trace-AI's Core Features
Real-time SBOM generation in CycloneDX and SPDX from CI
Direct and transitive dependency tracking across ecosystems
Exploit-aware vulnerability scoring beyond CVE lists
License compliance detection for GPL, LGPL, and other copyleft licenses
Vendor visibility including APIs, SDKs, SLA expiry, and breach history
Compliance mapping to ISO 27001, SOC 2, PCI-DSS, HIPAA, and GDPR
Open, auditable ZSBOM logic and forkable policy-as-code
Audit-ready exports as CycloneDX, SPDX, and JSON
How to use Trace-AI?
Connect: Link your GitHub or GitLab repository.
Scan: Let Trace-AI analyze dependencies and generate a live SBOM.
Monitor: Track vulnerabilities, licenses, and vendors in one dashboard.
Export: Generate audit-ready reports in CycloneDX, SPDX, or JSON.
Trace-AI's Use Cases
- Supply-chain visibility
- Vulnerability prioritization
- License compliance
- Audit readiness
- Vendor risk tracking