Description
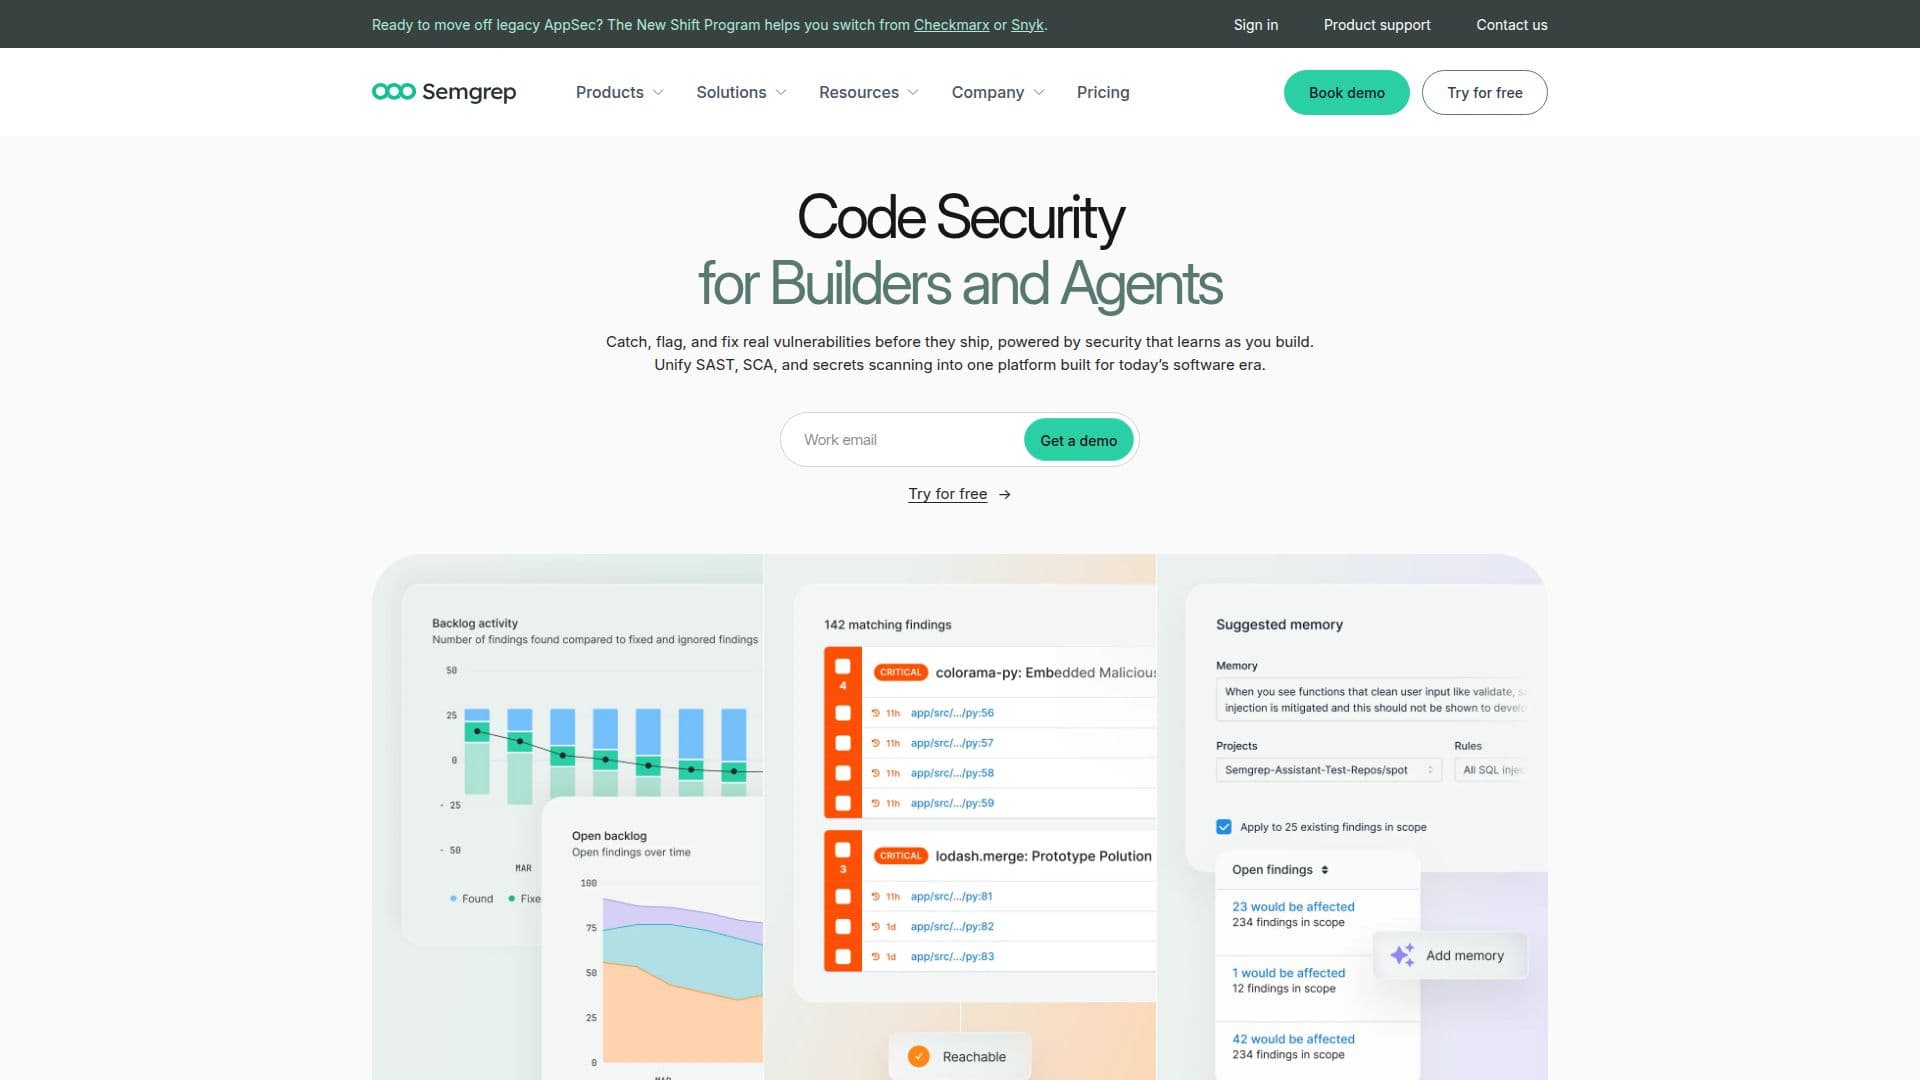
The Semgrep App Security Platform is designed to enhance application security by providing developers with tools to identify and remediate vulnerabilities in their code. It utilizes AI-assisted Static Application Security Testing (SAST), Software Composition Analysis (SCA), and Secrets Detection to surface true security issues that matter.
Read More
Semgrep Code helps developers find and fix vulnerabilities in their code, while Semgrep Supply Chain addresses vulnerabilities in open-source dependencies. The platform also includes Semgrep Secrets, which detects hardcoded secrets through semantic analysis. Additionally, Semgrep Guardian scans AI-generated code to ensure security as it is written.
One of the key features of Semgrep is its multimodal detection capability, which combines AI reasoning with rule-based analysis. This allows for more accurate detection, triage, and remediation of security issues. The platform automates security processes, enabling organizations to manage and enforce security policies effectively.
Semgrep also supports building and deploying security pipelines that integrate static analysis with AI at scale, making it suitable for organizations looking to enhance their security posture without slowing down development. The platform is designed for developers, AppSec teams, and CISOs, providing clear, actionable findings and measurable security outcomes.
With a focus on reducing false positives, Semgrep enables teams to prioritize real risks and streamline their workflows. The platform is built for modern software development environments, integrating seamlessly with popular CI/CD tools and IDEs. By leveraging Semgrep, organizations can ensure that security is embedded in their development processes, allowing for faster and more secure code delivery.
- CategoryAI Cybersecurity Tools
- Pricing ModelFreemium
- DeploymentCloud
- PlatformsWeb
Semgrep App Security Platform's Core Features
AI-assisted SAST
SCA for open-source dependencies
Secrets Detection
Multimodal detection
Automated security workflows
Integration with CI/CD tools
Real-time vulnerability scanning
Actionable remediation guidance
How to use Semgrep App Security Platform?
Configure: Set up Semgrep with your code repositories.
Integrate: Connect Semgrep with your CI/CD pipeline.
Scan: Run scans on your code to identify vulnerabilities.
Review: Analyze the findings and prioritize issues.
Remediate: Implement the suggested fixes in your code.
Monitor: Continuously scan and monitor for new vulnerabilities.
Optimize: Adjust settings and rules based on team feedback.
Semgrep App Security Platform's Use Cases
- Code Vulnerability Scanning
- Open Source Dependency Management
- Secrets Detection
- AI-Generated Code Security
- Continuous Security Integration