Description
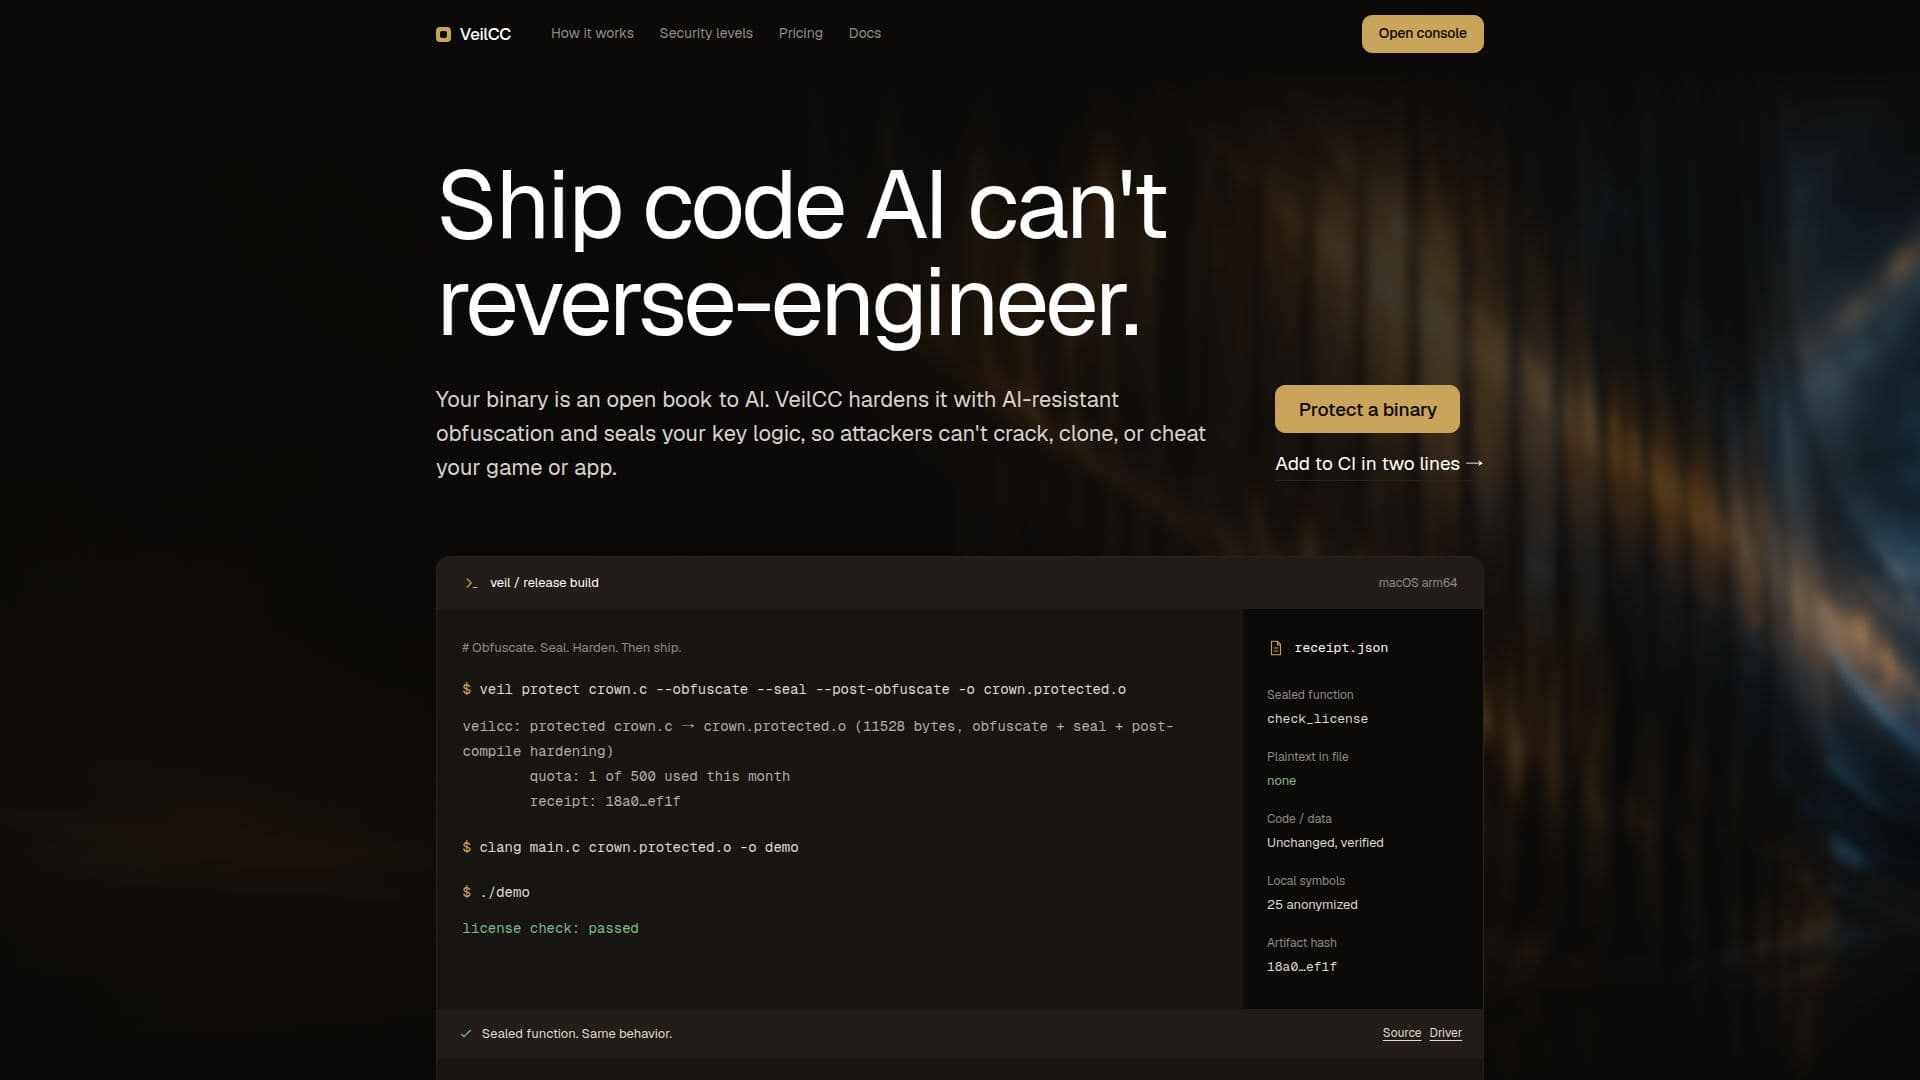
VeilCC provides advanced software protection designed to counter AI-driven reverse-engineering and traditional attack methods. The platform addresses the vulnerability of binaries, which can be easily analyzed by AI agents to expose critical logic like license checks, cheat detection routines, or pricing models. VeilCC employs a multi-layered approach, combining obfuscation and logic sealing to harden applications and games.
Read More
The core of VeilCC's protection lies in its sealing mechanism. Instead of merely rearranging code, sealing removes designated "crown jewel" functions from the shipped binary, storing them as ciphertext. These functions are only decrypted and executed in cleartext for microseconds at the exact moment they are called, then immediately scrubbed from memory. This makes static analysis, sandboxing, and off-device dumps ineffective, as the critical logic simply isn't present in the file at rest.
Users can integrate VeilCC into their build pipelines or use a drag-and-drop console. The process involves marking specific functions for protection, which can be done in source code or by naming symbols at build time. VeilCC supports various protection levels, including module-wide obfuscation and function-specific sealing. For enhanced security, device-bound keys can be utilized, ensuring that a copied binary cannot decrypt its sealed functions on another machine, effectively preventing redistribution and emulated servers.
VeilCC is designed to be language-agnostic, working with anything that compiles through LLVM, including C, C++, Rust, and Swift on macOS, Linux, and Windows. It offers a free tier for trying out obfuscation and sealing on personal binaries, with paid plans providing more protected builds, moving-target seeds, and advanced features like hosted Protection API and GitHub Actions. Enterprise solutions include device-bound seal keys, on-premise Protection API, and license/activation APIs, catering to industries like fintech, firmware, and games. VeilCC emphasizes measurable security, providing a build receipt detailing the applied protection layers and artifact hash.
- CategoryAI Cybersecurity Tools
- Pricing ModelFreemium
- DeploymentCloud, On-Premise
- PlatformsmacOS, Linux, Windows
VeilCC's Core Features
AI-Resistant Obfuscation: Misleads AI decompilers with mixed-boolean arithmetic and opaque-predicate/honeypot decoys.
Logic Sealing: Removes critical functions from the binary, shipping them as ciphertext.
Runtime Decryption & Scrubbing: Functions decrypt only at call time into W^X pages, then are immediately scrubbed.
Device-Bound Keys: Links decryption keys to a device's secure enclave/TPM, preventing copied binaries from running.
Moving-Target Seed: Generates a fresh protection seed for every build, increasing attack difficulty.
Build Receipt: Provides a verifiable record of sealed functions, protection layers, and artifact hash.
CLI Integration: Protects any object with a single command, integrating into existing link steps.
Pipeline Integration: Adds two lines to build pipelines for server-side protection with fresh seeds.
Drag & Drop Console: Allows users to scan and protect binaries without installation.
Language Agnostic: Works with any language compiling through LLVM (C, C++, Rust, Swift verified).
Post-Compile Hardening: Strips debug metadata and randomizes private names to remove analysis hints.
Anti-Debug Checks: Folds debugger-present checks into the key, causing decryption to garbage if traced.
Configurable Protection Levels: Stack obfuscation and sealing, with embedded or device-bound keys.
Hot Path Refusal: Automatically prevents sealing of performance-critical functions to maintain frame budget.
On-Premise Deployment: Enterprise option for running Protection API within a private network.
How to use VeilCC?
Build as Normal: Compile your application or game as you typically would.
Mark Crown Jewel Functions: Identify critical functions (e.g., license checks, anti-cheat) and mark them for protection in source or by symbol list.
Set Protection Level: Choose between module-wide obfuscation, function sealing, or both, and select key embedding or device-bound keys.
Integrate VeilCC: Use the drag-and-drop console, CLI, or add two lines to your CI/CD pipeline.
Generate Protected Build: VeilCC processes your compiled objects server-side, returning a hardened binary.
Ship Protected Code: Deploy your application with AI-resistant obfuscation and sealed logic.
VeilCC's Use Cases
- Protect License Checks
- Harden Anti-Cheat Systems
- Secure Proprietary Kernels
- Digital Rights Management (DRM)
- Prevent Software Cloning
- Protect Pricing Models
- Firmware Security
- Fintech Application Security
- Attestation Routines