Description
OpenCode Code Review provides automated AI-driven pull request reviews directly within your GitHub Actions environment. This free and open-source tool integrates seamlessly into your development workflow, offering a read-only analysis of every pull request. It's designed to identify potential defects and suggest fixes, enhancing code quality and streamlining the review process.
Read More
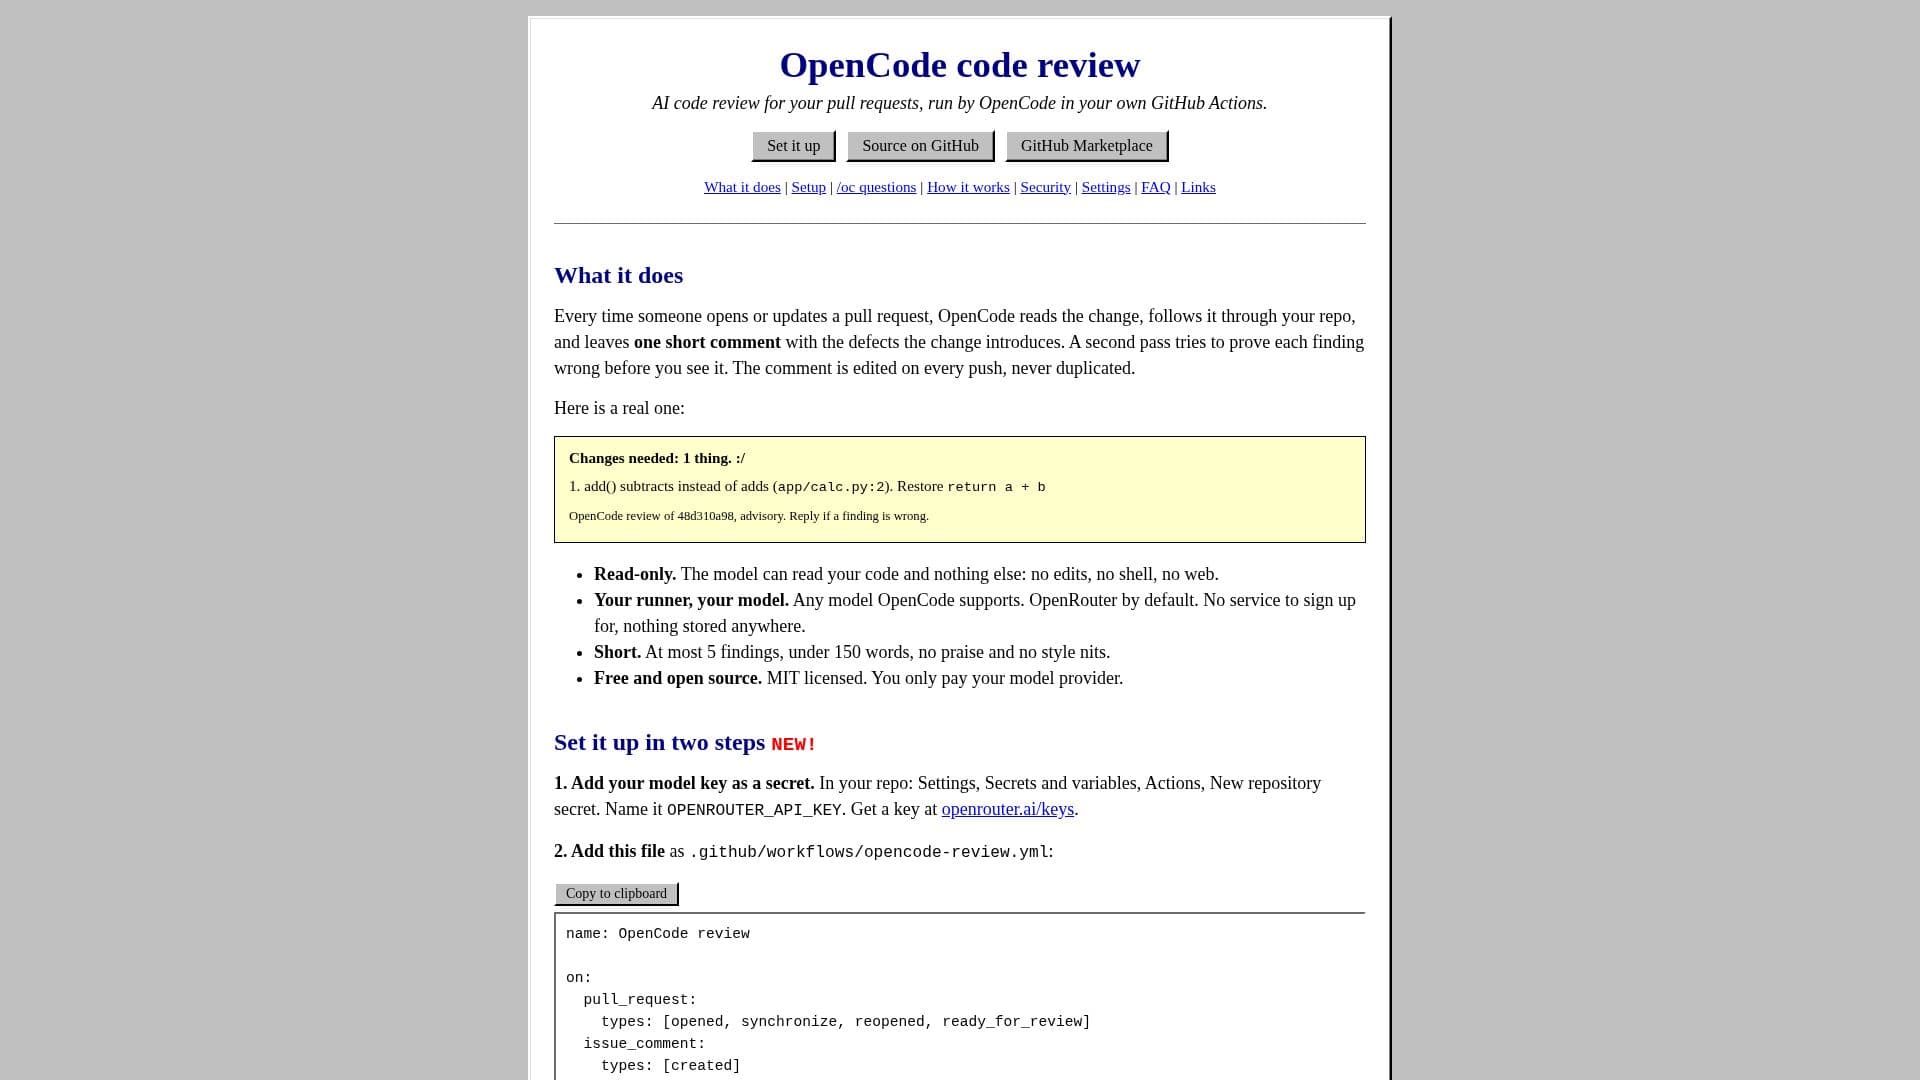
The action operates by reading code changes, following them through your repository, and then posting a concise comment detailing any introduced defects. A unique two-pass system ensures accuracy: after an initial scan, a second pass attempts to refute each finding, ensuring only validated issues are presented. The review comment is dynamically updated with every push, preventing duplication and keeping feedback current.
Users maintain full control over their data and models. The tool runs in your own GitHub Actions with your own model key, supporting a variety of providers including OpenRouter (default), Anthropic, OpenAI, and Google. This architecture ensures no data is stored externally and no third-party service sign-up is required. The action is strictly read-only, meaning it cannot modify code, approve pull requests, or execute shell commands, prioritizing security and preventing unintended changes.
Beyond automated reviews, OpenCode Code Review allows team members to interact with the AI reviewer using `/oc` commands. By commenting `/oc why does this retry twice?` or `/oc review` on any issue or pull request, users can get detailed answers with file:line references or trigger a re-review. This interactive capability is restricted to repository owners, members, and collaborators, ensuring controlled access.
Setup is straightforward, involving adding your model key as a repository secret and integrating a workflow file. The tool also supports custom guidance through a `guide.md` file, allowing the reviewer to understand project specifics and coding rules. This ensures the AI focuses on relevant aspects of your codebase, providing more targeted and effective feedback. The action is MIT licensed, meaning users only incur costs from their chosen model provider for token usage and GitHub for runner minutes, if applicable.
- CategoryAI Code Review & Testing
- Pricing ModelFree
- DeploymentGitHub Actions
- PlatformsWeb
OpenCode Code Review's Core Features
Automated AI pull request reviews
Runs within your own GitHub Actions
Supports multiple AI model providers (OpenRouter, Anthropic, OpenAI, Google)
Read-only operation for enhanced security
Two-pass defect validation system
Dynamic review comments updated on every push
Interactive `/oc` commands for questions and re-reviews
Customizable project guidance via `guide.md`
Skipped reviews for fork pull requests to protect model keys
Self-hosted runner support for private repositories
Configurable review budget and maximum findings
MIT licensed and open source
Excludes lockfiles, translations, and minified files from review
Security measures against prompt injection and unauthorized access
Benchmarking tools for evaluating model and prompt changes
How to use OpenCode Code Review?
Add Model Key: Create a new repository secret named `OPENROUTER_API_KEY` (or for your chosen provider) in your GitHub repository settings.
Add Workflow File: Create `.github/workflows/opencode-review.yml` in your repository with the provided workflow configuration.
Open Pull Request: Open a pull request to trigger an automated AI code review.
Receive Review: A review comment with identified defects will appear on your pull request within minutes.
Ask Questions: Comment `/oc <question>` on any issue or pull request to get AI-generated answers with code references.
Re-run Review: Comment `/oc review` on a pull request to re-run the AI review and update the existing comment.
Customize Review: Copy `templates/guide.md` to `.github/opencode-review/guide.md` and add project-specific guidelines for smarter reviews.
OpenCode Code Review's Use Cases
- Automated Code Quality Checks
- Streamlined Code Review Process
- Developer Education and Feedback
- Security Vulnerability Detection
- On-Demand Code Explanation
- Customizable Review Guidelines
- Open-Source Project Maintenance
- Private Repository Code Security