Description
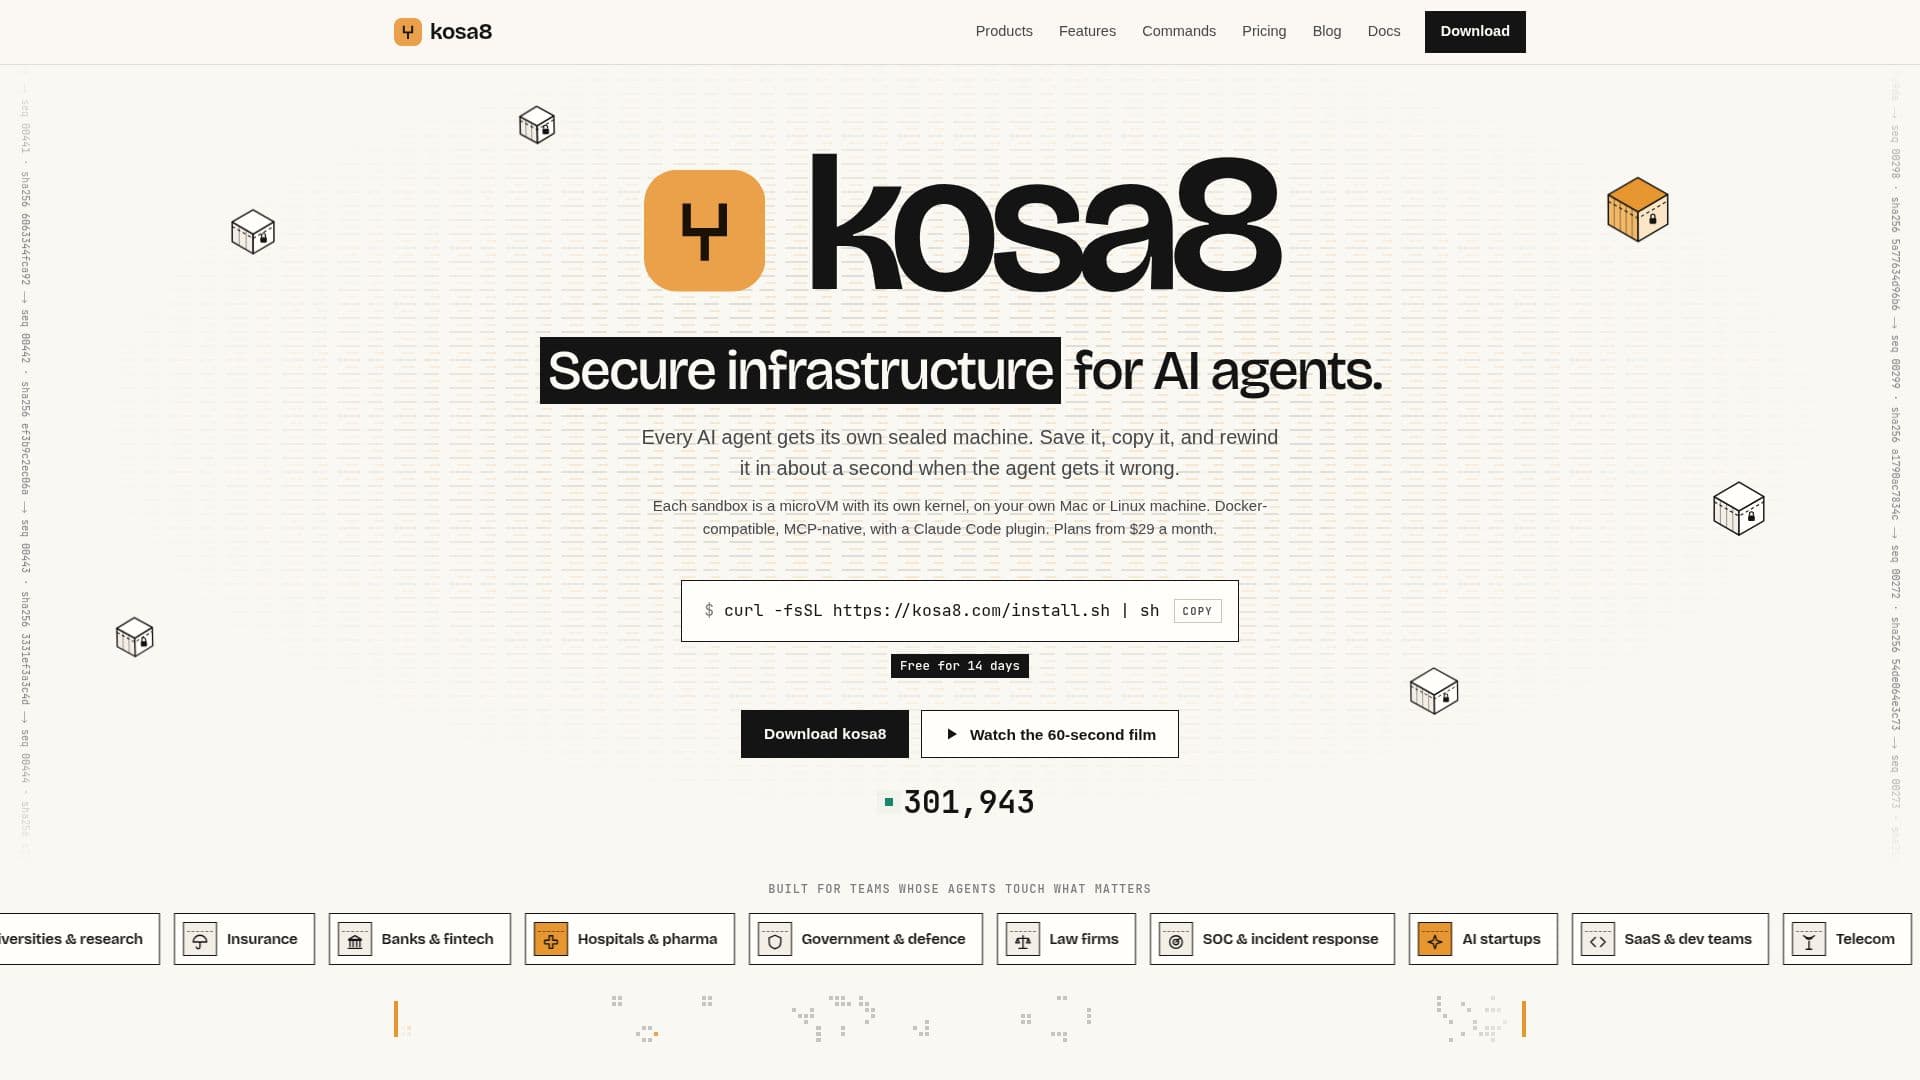
Kosa8 offers secure microVM sandboxes designed specifically for AI agents, running natively on Mac and Linux machines. Each AI agent operates within its own sealed microVM, providing a robust isolation boundary that prevents unauthorized access to the host system. This architecture allows users to checkpoint, rewind, and fork agent environments in approximately one second, enabling rapid iteration and recovery from errors without compromising system integrity.
Read More
The platform is built for teams whose AI agents interact with sensitive data, including those in banking, fintech, healthcare, pharma, government, defense, and legal sectors. It addresses critical security concerns by ensuring that API keys remain on the host machine, with sandboxes holding only placeholders. The network within each sandbox is closed by default, allowing only explicitly allow-listed hosts, and all network rules are enforced on the host side, beyond the agent's reach.
Key capabilities include the ability to give every task its own isolated machine, which can be forked into multiple live copies for parallel experimentation. This is particularly useful for detonating malware samples in a controlled environment or training analysts on disposable machines that reset in seconds. Kosa8 also facilitates audit compliance by providing a hash-chained record of every action, distinguishing between human and agent activities, and requiring human approvals for risky operations. It supports FIPS 140-3 builds and offers offline licensing options for air-gapped environments.
Kosa8 is Docker-compatible, allowing existing tooling to integrate seamlessly. It provides built-in kits for popular coding agents like Claude Code, OpenAI Codex CLI, Gemini CLI, and OpenCode, as well as support for agent frameworks such as LangGraph and CrewAI. The platform enables local model execution with OpenAI- and Anthropic-compatible APIs, ensuring data privacy and eliminating token-based billing. Installation is straightforward, typically a single command, and a 14-day free trial is available without requiring a credit card or account.
Pricing plans are structured based on concurrent copies rather than seats, starting from $29 per month for individual users and scaling up for teams and large fleets. Capacity add-ons are available for larger sandbox requirements. Kosa8 emphasizes transparency and verifiability, with usage counts derived from a tamper-evident audit log stored on the user's machine, which can be independently verified. The software has no telemetry, crash reporting, or analytics, reinforcing its commitment to privacy and security.
- CategorySecurity & Privacy
- Pricing ModelPaid
- DeploymentLocal (Mac, Linux, Windows WSL2)
- PlatformsmacOS, Linux, Windows 11 (WSL2)
Kosa8's Core Features
Secure microVM sandboxes for AI agents
Checkpoint, rewind, and fork agent environments in seconds
Closed, allow-listed network enforced on the host
API keys kept outside the sandbox with egress brokering
Tamper-evident, hash-chained audit trail for all actions
Human approval gates for risky operations
Support for local AI models with OpenAI/Anthropic-compatible API
Docker-compatible API for existing tooling
Built-in kits for Claude Code, Codex CLI, Gemini CLI, OpenCode
FIPS 140-3 builds and offline licensing for regulated environments
Scalable plans based on concurrent agent copies
No telemetry, crash reporting, or analytics
Supports Apple Silicon Macs, x86-64 Linux, and Windows 11 (WSL2)
Ability to run multiple AI agent approaches in parallel
Signed releases and verifiable downloads
How to use Kosa8?
Install Kosa8: Use a single command to install Kosa8 on your Mac or Linux machine.
Check machine readiness: Run a command to verify your system configuration and address any issues.
Run an AI agent: Launch a coding agent within its own sealed microVM, ensuring isolation.
Manage agent state: Checkpoint the running machine before risky actions and rewind if something goes wrong.
Control network access: Define allow-listed hosts for the agent's network, enforced by the host.
Secure API keys: Utilize the egress broker to provide API keys without exposing them inside the sandbox.
Approve risky actions: Implement human approval workflows for destructive or escalating agent commands.
Monitor and audit: Review the hash-chained audit log to track all agent activities and decisions.
Kosa8's Use Cases
- Secure AI Agent Development
- Financial Services Compliance
- Healthcare Data Protection
- Government & Defense Operations
- Legal Client Confidentiality
- Security Operations & Incident Response
- Parallel AI Agent Experimentation
- Unattended AI Agent Workflows
- Local LLM Execution
- Auditable AI Deployments