Description
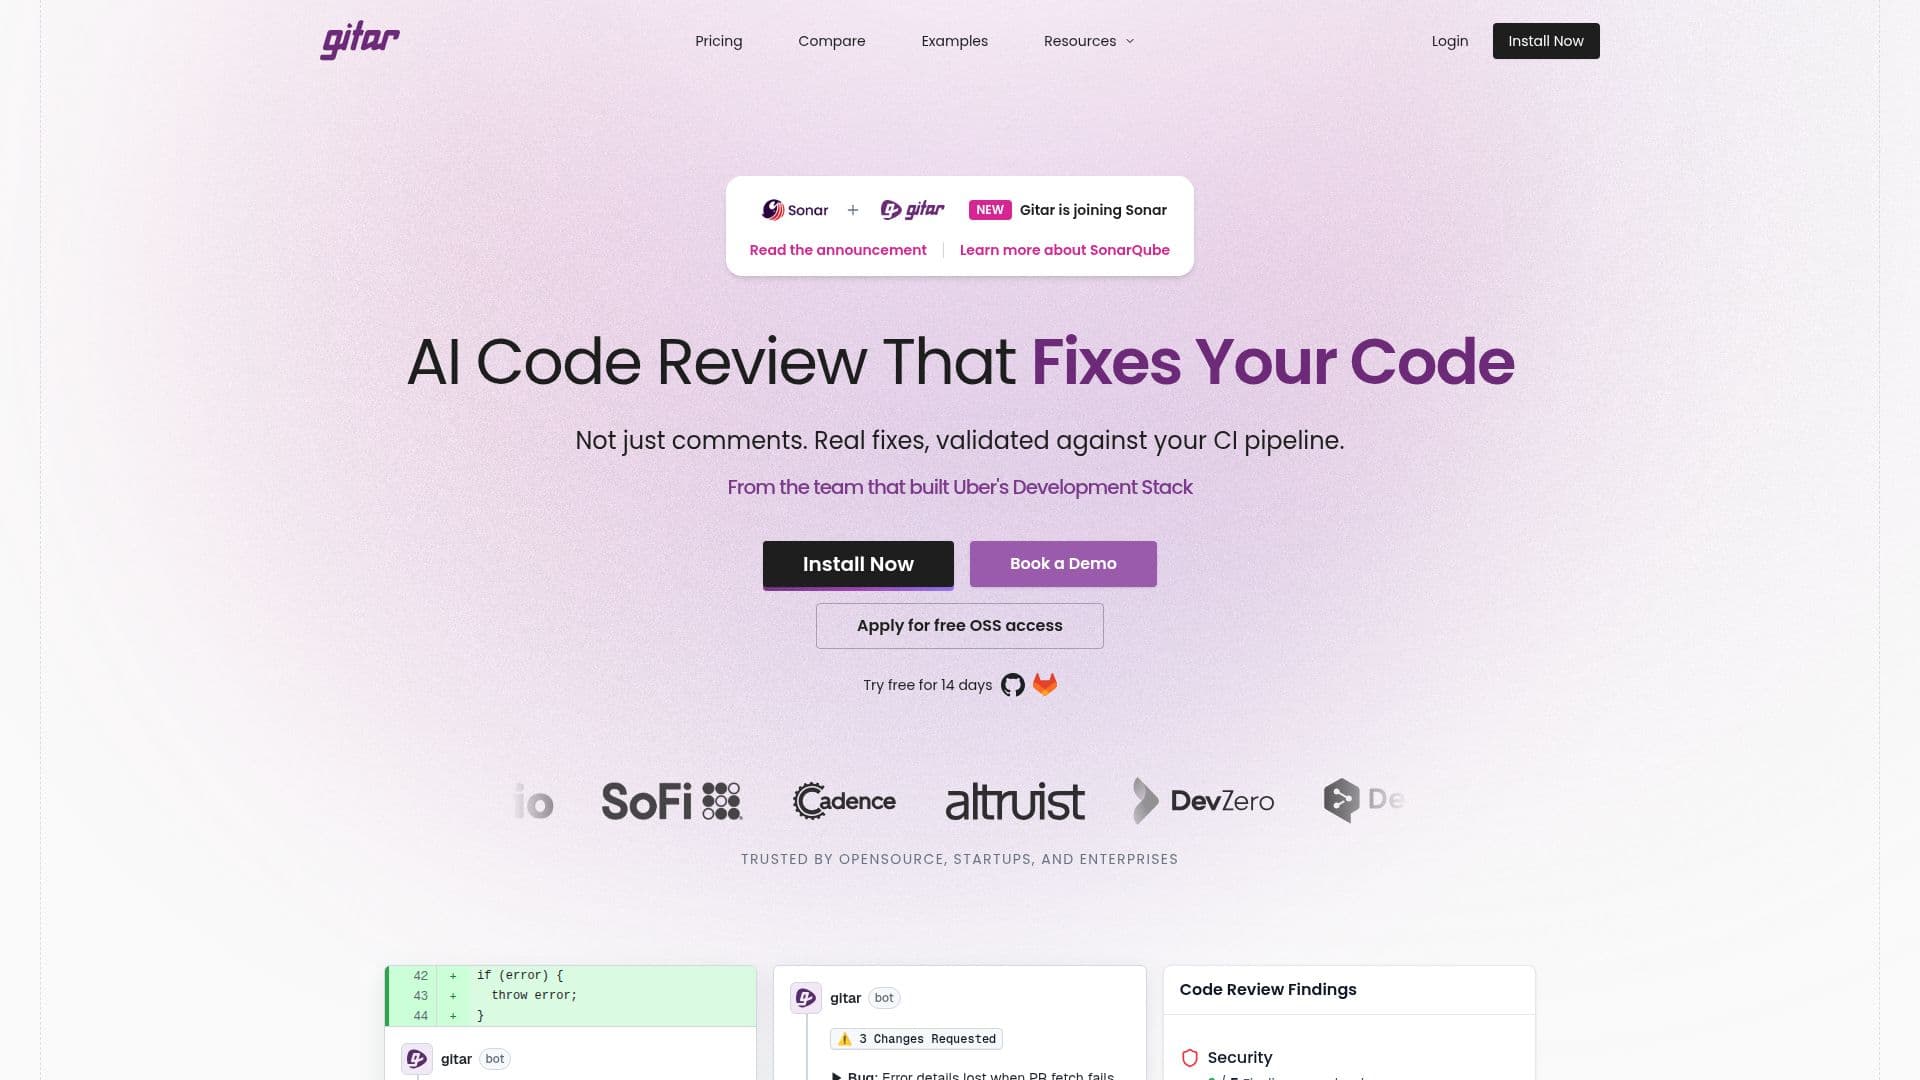
Gitar is a code change verification agent built by Sonar, the company behind SonarQube. Its pitch is "don't just review, ship": rather than only leaving comments on a pull request, Gitar is meant to take a change from opened to merge-ready and show proof that it passed.
Read More
Gitar reviews each pull request with context on the codebase and team conventions, tuned to flag issues it considers real rather than burying a PR in comments, with one consolidated comment and inline notes only where they matter. When CI fails, it reads the pipeline output, separates genuine breakage from flaky tests or infrastructure noise, and root-causes what went wrong instead of leaving a raw log dump. When it finds a fixable problem, it generates the fix and commits it to the branch under rules the team defines: what Gitar may fix on its own, what it must escalate, and what blocks a merge outright. It then iterates until CI is green and commits only at that point. An analytics dashboard tracks time to merge, fix rates, and CI failure patterns over time.
Gitar connects to GitHub, GitLab, Bitbucket, and Azure DevOps for source control, and to CircleCI, Buildkite, Bitrise, Harness, TeamCity, and Jenkins for CI, plus Jira, Linear, and Slack. On data handling, Sonar states Gitar does not retain source code, does not use customer code to train models, and holds zero data retention agreements with its LLM providers; users can optionally bring their own Anthropic API key. It is SOC 2 Type II certified, ISO 27001 certified, and GDPR verified.
Sonar positions Gitar as a complement to SonarQube rather than a replacement: SonarQube runs deterministic, rule-based analysis across more than 40 languages for code quality, security vulnerabilities, and technical debt, while Gitar adds AI-native review that reasons about the intent and logic of a change, catching functional bugs SonarQube's static rules would not. Gitar is priced per user: Core at $20 per user per month and Pro at $40 per user per month, with Enterprise available at custom, outcome-based pricing charged per pull request. A 14-day free trial of the Pro plan is available with no credit card required.
- CategoryAI Code Review & Testing
- Pricing ModelFreemium
- DeploymentCloud
- PlatformsGitHub, GitLab
Gitar's Core Features
Reviews pull requests with codebase and convention context, tuned for a low false-positive rate
Diagnoses CI failures and separates real breakage from flaky tests or infrastructure noise
Generates and commits fixes automatically within rules a team defines
Iterates on a change until CI passes, then commits only on a green pipeline
Lets teams write merge policy in plain language to control what Gitar may fix or must escalate
Provides analytics on time to merge, fix rates, and recurring failure patterns
Integrates with GitHub, GitLab, Bitbucket, Azure DevOps, and major CI providers
Holds SOC 2 Type II, ISO 27001, and GDPR certification with zero data retention
How to use Gitar?
Connect your repo and CI: Link GitHub, GitLab, Bitbucket, or Azure DevOps and your CI provider.
Set your merge policy: Define in plain language what Gitar may fix, escalate, or block.
Let it review: Gitar comments on real issues and reads CI results on each pull request.
Review proposed fixes: Approve or adjust the fixes Gitar commits under your rules.
Merge on green: Gitar iterates until CI passes before the change is marked ready.
Track the trend: Use the analytics dashboard to watch merge time and fix rates over time.
Gitar's Use Cases
- Pull request review
- CI failure triage
- Autonomous bug fixes
- Agentic code review at scale