ToolPotion
AI Advisor
Submit a Tool (Free)

Machine Learning for Hackers

Machine Learning for Hackers is a comprehensive course that teaches how to attack and defend machine learning systems using real-world hacking techniques. It covers setting up an ML hacking lab, interacting with models, and understanding vulnerabilities.

View Course
Share
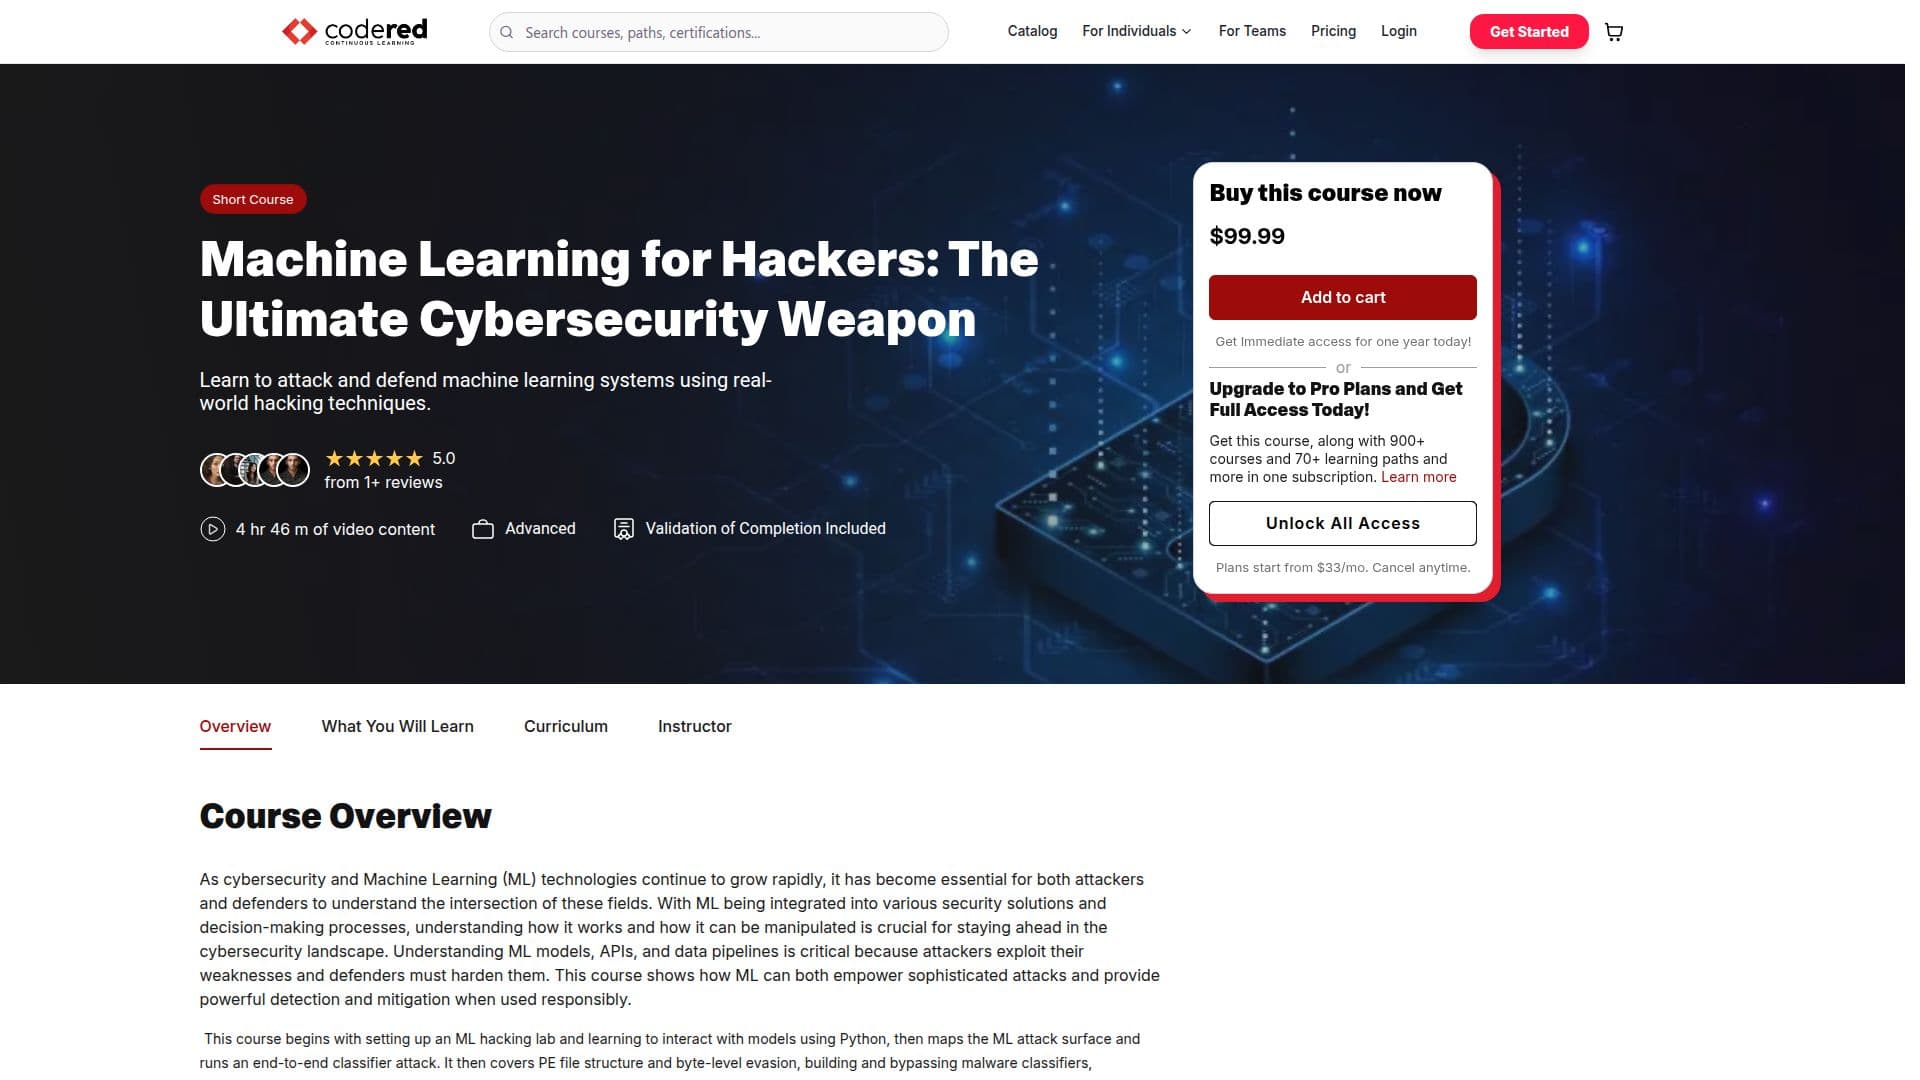
Machine Learning for Hackers screenshot

Machine Learning for Hackers is a course designed to equip cybersecurity professionals with the skills needed to both attack and defend machine learning systems. As ML technologies become integral to security solutions, understanding their vulnerabilities is crucial. This course begins with setting up an ML hacking lab and learning to interact with models using Python. Participants will map the ML attack surface and conduct end-to-end classifier attacks. The curriculum covers PE file structure and byte-level evasion, building and bypassing malware classifiers, and automating phishing and social engineering with language models. It also includes deepfake creation and detection, behavioral analysis, adversarial ML techniques, smart fuzzing for vulnerability discovery, and model stealing, poisoning, watermarking, and backdoors. By the end of the course, learners will be able to test and secure ML systems, craft and detect adversarial samples, and apply effective model defense strategies. The course is taught by Tshering Tobzang, a senior cybersecurity officer with expertise in adversarial machine learning and automated threat detection. This course is ideal for cybersecurity professionals looking to expand their expertise in ML-based security solutions.

  • CategoryEducation & Research
  • Pricing ModelSubscription

  • Set up an ML hacking lab

  • Interact with ML models using Python

  • Map the ML attack surface

  • Conduct end-to-end classifier attacks

  • Modify PE files for evasion

  • Automate phishing with language models

  • Perform adversarial ML techniques

  • Explore model theft and backdoor attacks

  1. Set up: Configure your ML hacking lab

  2. Interact: Use Python to engage with ML models

  3. Map: Identify the ML attack surface

  4. Conduct: Execute end-to-end classifier attacks

  5. Modify: Alter PE files to evade detection

  6. Automate: Use language models for phishing

  7. Perform: Conduct adversarial ML attacks

  8. Explore: Investigate model theft and backdoors

  • ML System Security
  • Adversarial Attacks
  • Phishing Automation
  • Deepfake Detection
  • Model Theft Prevention

Machine Learning for Hackers Reviews

Loading...

Similar to Machine Learning for Hackers

Springboard's Machine Learning & AI Bootcamp is a 6-month online program designed to teach students machine learning, deep learning, and AI. With 1:1 mentoring, students build and…

Education & Research
View Tool

Machine Learning & AI Bootcamp is a 6-month online program designed to teach students machine learning, deep learning, and AI. With 1:1 mentoring, students build and…Springboard's Machine Learning & AI Bootcamp is a 6-month online program designed to teach students machine learning, deep learning, and AI. With 1:1 mentoring, students build and…

Education & Research
See the Top 100 AI Learning

Adversarial Robustness Toolbox is a Python library designed to enhance the security of machine learning models. It offers tools for evaluating, defending, and verifying models…

AI Cybersecurity Tools

Ranked #34 in AI Frameworks

View Tool

Python library designed to enhance the security of machine learning models. It offers tools for evaluating, defending, and verifying models…Adversarial Robustness Toolbox is a Python library designed to enhance the security of machine learning models. It offers tools for evaluating, defending, and verifying models…

AI Cybersecurity Tools
Ranked #34 in AI Frameworks

AgentDojo

AI Frameworks

AgentDojo is a dynamic environment designed to evaluate prompt injection attacks and defenses for LLM agents. Developed by researchers from ETH Zurich and Invariant Labs, it…

AI Cybersecurity Tools
View Tool

AI Frameworks

Dynamic environment designed to evaluate prompt injection attacks and defenses for LLM agents. Developed by researchers from ETH Zurich and Invariant Labs, it…AgentDojo is a dynamic environment designed to evaluate prompt injection attacks and defenses for LLM agents. Developed by researchers from ETH Zurich and Invariant Labs, it…

AI Cybersecurity Tools
See the Top 50 AI Frameworks

Giskard

AI Apps

Giskard is an AI security platform focused on continuous red teaming and LLM security. It helps detect vulnerabilities, prevent hallucinations, and safeguard AI systems through…

AI Cybersecurity Tools

Ranked #94 for Monitoring AI models

View Tool

AI Apps

AI security platform focused on continuous red teaming and LLM security. It helps detect vulnerabilities, prevent hallucinations, and safeguard AI systems through…Giskard is an AI security platform focused on continuous red teaming and LLM security. It helps detect vulnerabilities, prevent hallucinations, and safeguard AI systems through…

AI Cybersecurity Tools
Ranked #94 for Monitoring AI models

Modelscan is a GitHub project focused on protecting against model serialization attacks. It provides tools and resources for developers to secure their machine learning models…

AI Cybersecurity Tools
View Tool

GitHub project focused on protecting against model serialization attacks. It provides tools and resources for developers to secure their machine learning models…Modelscan is a GitHub project focused on protecting against model serialization attacks. It provides tools and resources for developers to secure their machine learning models…

AI Cybersecurity Tools
See the Top 250 AI GitHub Repos

garak is an open-source LLM vulnerability scanner designed to assess the security of large language models. It offers numerous plugins and thousands of prompts to test model…

AI Cybersecurity Tools

Ranked #27 in AI Frameworks

View Tool

Open-source LLM vulnerability scanner designed to assess the security of large language models. It offers numerous plugins and thousands of prompts to test model…garak is an open-source LLM vulnerability scanner designed to assess the security of large language models. It offers numerous plugins and thousands of prompts to test model…

AI Cybersecurity Tools
Ranked #27 in AI Frameworks

Adversa AI

AI Apps

Adversa AI offers an autonomous platform for continuous AI red teaming, specifically designed for AI agents, LLMs, and GenAI applications. It identifies and remediates security…

AI Cybersecurity ToolsFinance & Banking

Ranked #119 for Monitoring AI models

View Tool

AI Apps

Offers an autonomous platform for continuous AI red teaming, specifically designed for AI agents, LLMs, and GenAI applications. It identifies and remediates security…Adversa AI offers an autonomous platform for continuous AI red teaming, specifically designed for AI agents, LLMs, and GenAI applications. It identifies and remediates security…

AI Cybersecurity ToolsFinance & Banking
Ranked #119 for Monitoring AI models

SkillSpector is a security scanner for AI agent skills, designed to detect vulnerabilities, malicious patterns, and security risks. It focuses on prompt injection, data…

AI Cybersecurity Tools
View Tool

Security scanner for AI agent skills, designed to detect vulnerabilities, malicious patterns, and security risks. It focuses on prompt injection, data…SkillSpector is a security scanner for AI agent skills, designed to detect vulnerabilities, malicious patterns, and security risks. It focuses on prompt injection, data…

AI Cybersecurity Tools
See the Top 250 AI GitHub Repos
1 of 8