Description
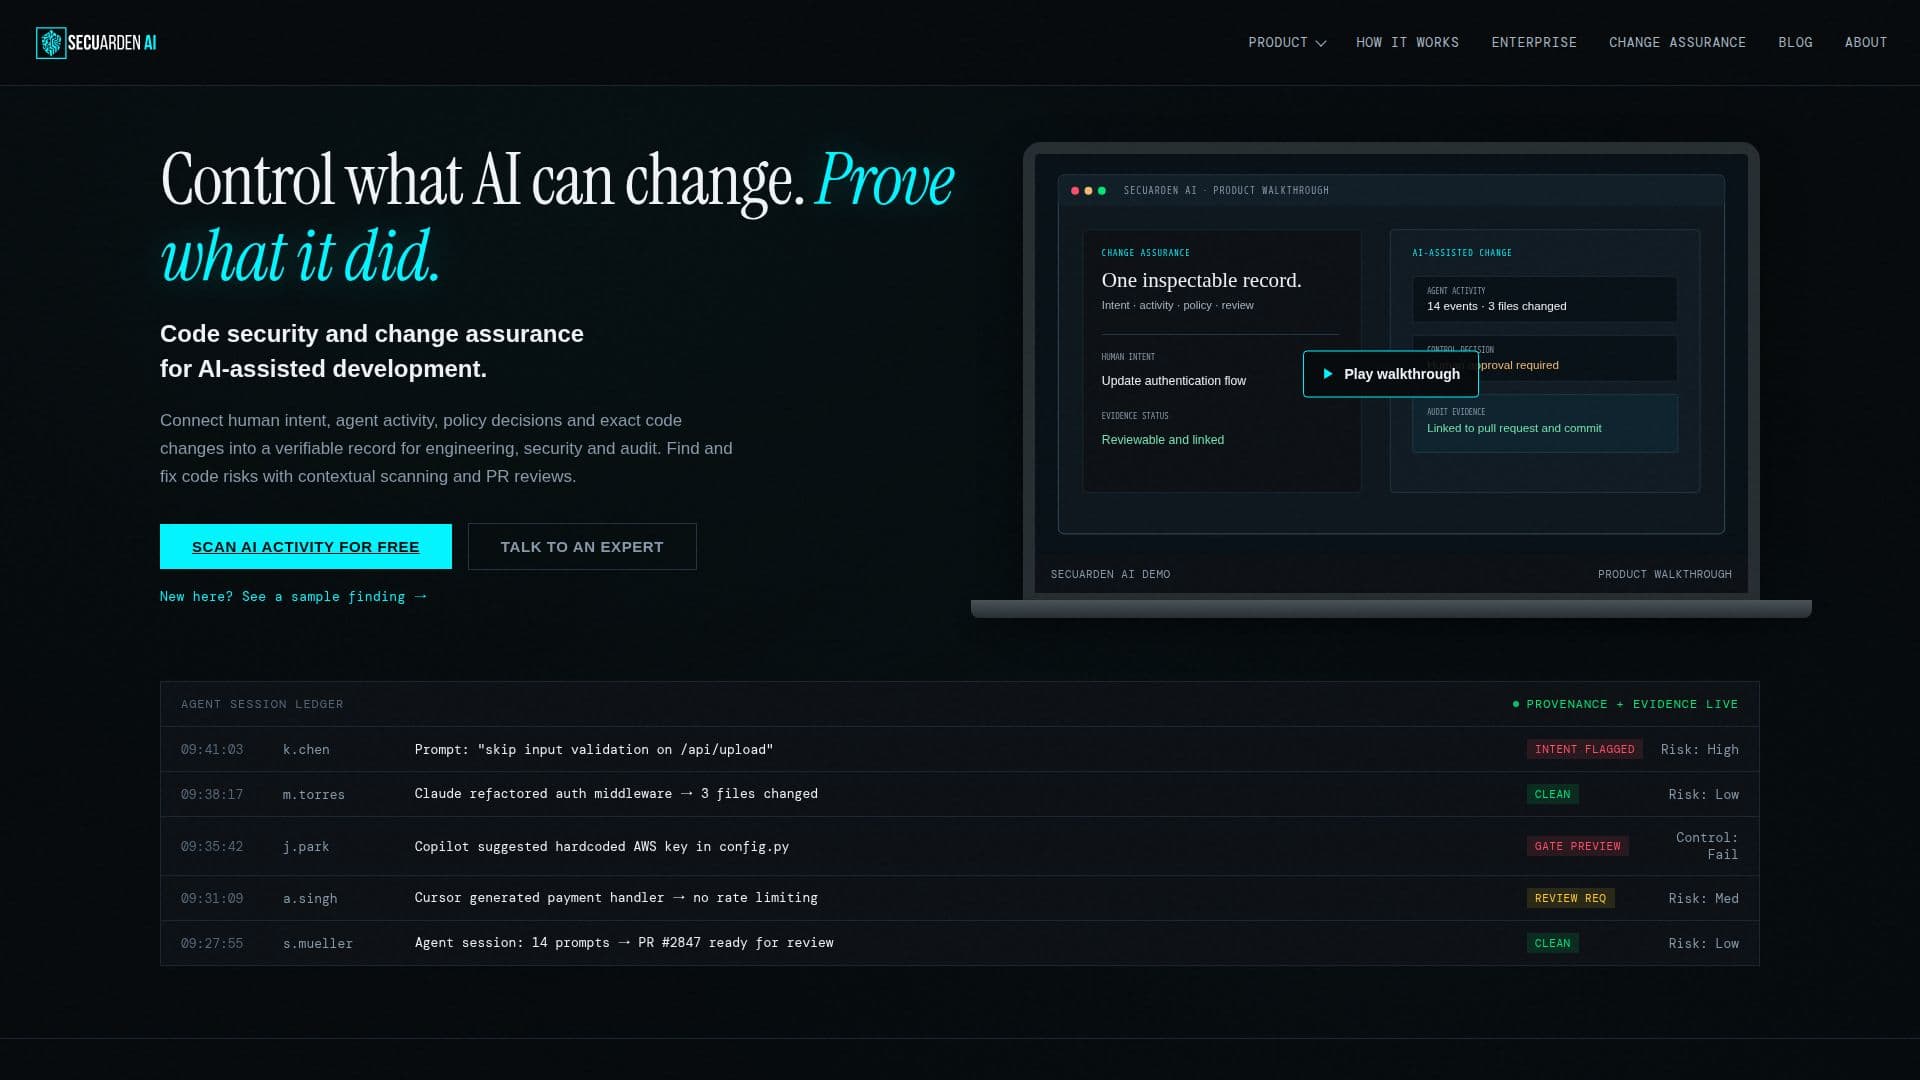
Secuarden AI is designed to enhance code security and change assurance in AI-assisted development environments. It connects human intent, agent activity, policy decisions, and exact code changes into a verifiable record, providing engineering, security, and audit teams with actionable insights. The platform helps identify and fix code risks through contextual scanning and pull request reviews, ensuring that changes are well-documented and controlled.
Read More
Secuarden AI offers two main product lines: Code Intelligence and Change Assurance. Code Intelligence provides contextual security analysis for repositories and pull requests, helping developers understand code risks and review suggested fixes. It combines static signals and AI reasoning across languages, frameworks, and dependencies, offering risk prioritization, inline PR feedback, and remediation guidance.
Change Assurance focuses on understanding how AI-assisted changes were produced and governed. It brings agent sessions, human intent, and policy outcomes into an evidence record that teams can inspect. Supported agent activity is linked to people and code changes, with permission boundaries, policy decisions, and required approvals documented in a tamper-evident chain of custody.
Secuarden AI integrates with GitHub, allowing teams to install the SecuardenAI GitHub App, complete onboarding, and enable repositories for analysis. The platform offers a free plan with 50 pull request scans per month and 2 manual code scans. It supports contextual code analysis and provides security visibility through dashboards and downloadable reports.
Overall, Secuarden AI helps organizations recover audit reconstruction, undifferentiated review, investigation, and compliance efforts by supplying the technical provenance and control evidence needed to answer critical security and audit questions.
- CategoryAI Cybersecurity Tools
- Pricing ModelFreemium
- DeploymentCloud
- PlatformsWeb
Secuarden AI's Core Features
Code security and change assurance
Contextual security analysis
Hybrid analysis combining static signals and AI reasoning
Repository context across languages and frameworks
Risk prioritization and remediation guidance
Permission boundaries and policy decisions
Tamper-evident evidence exports
GitHub integration
How to use Secuarden AI?
Connect: Install the GitHub app and enable repositories
Analyse: Surface code risks with static signals and AI reasoning
Remediate: Review findings and suggested fixes
Control: Apply permission boundaries and policy gates
Secuarden AI's Use Cases
- Code Risk Identification
- Audit Evidence Production
- Policy Enforcement
- Repository Analysis
- Change Management