Description
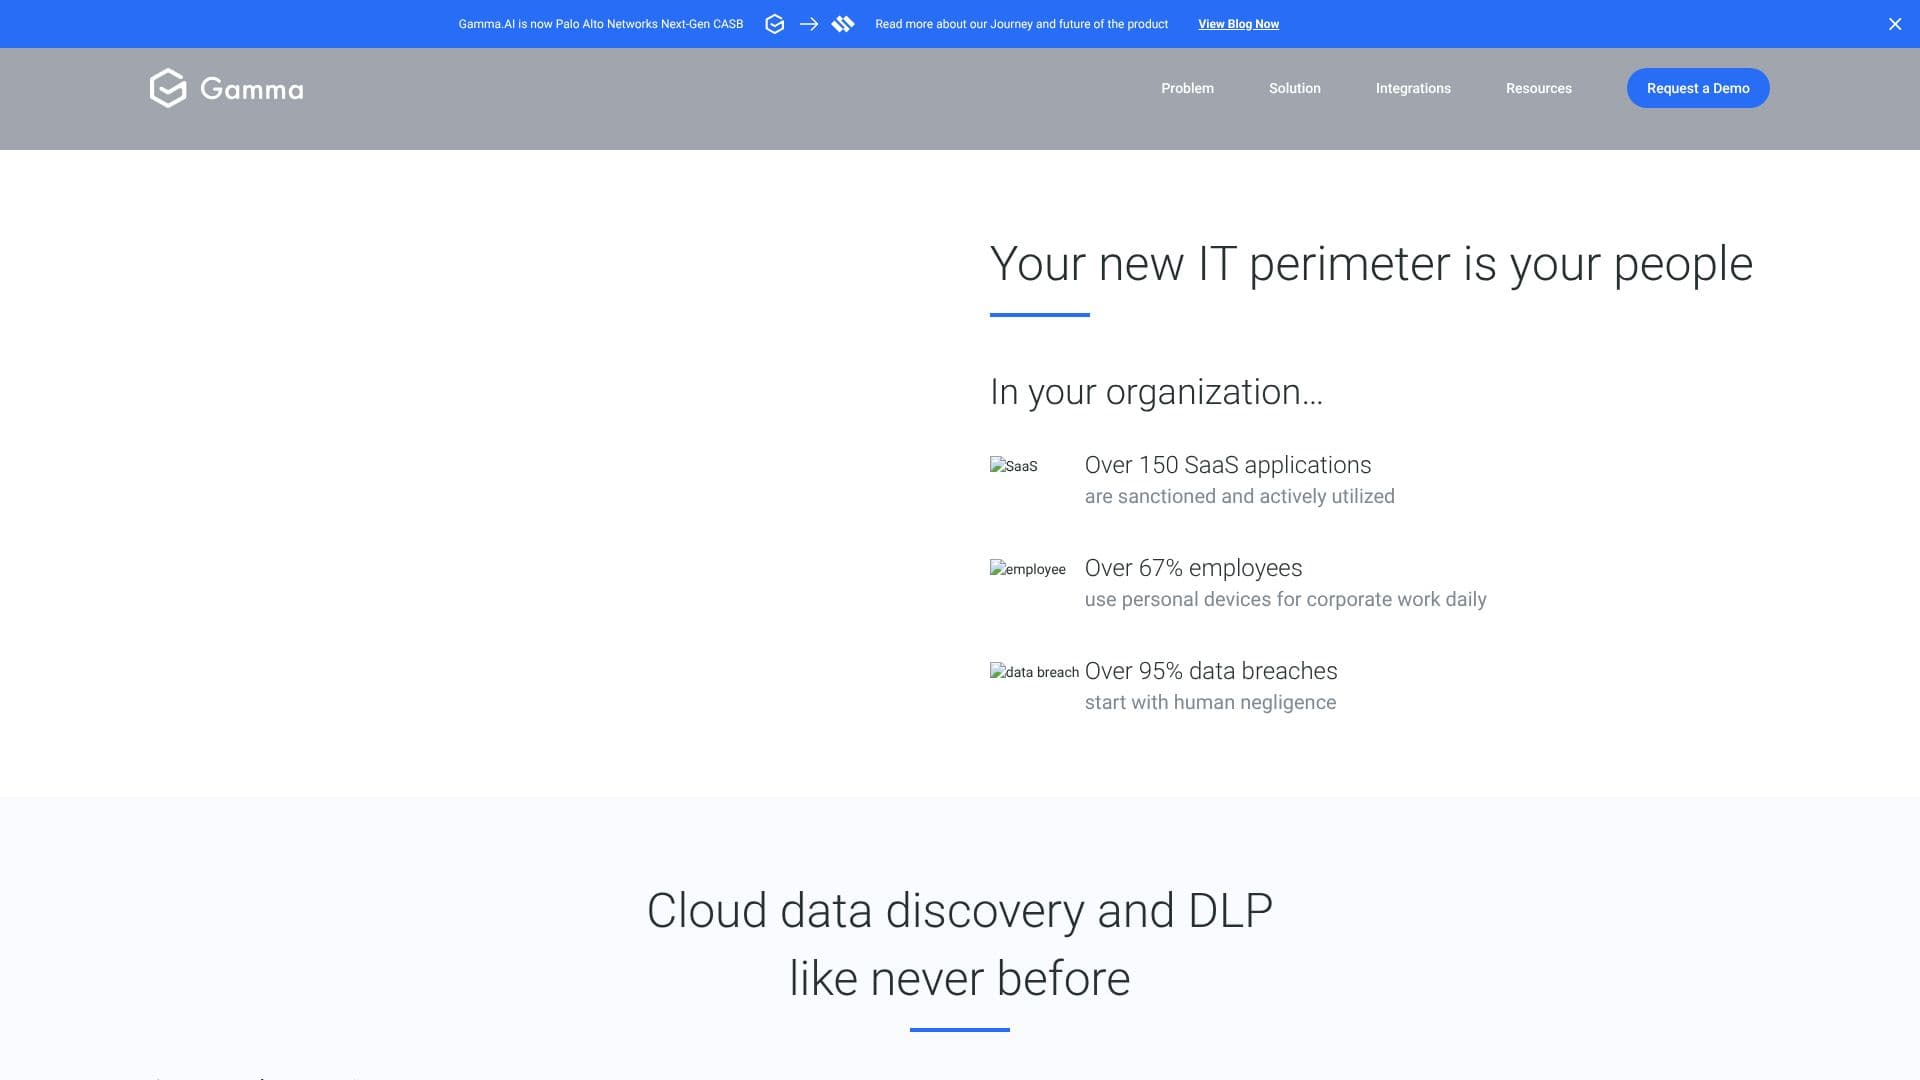
Gamma.AI launched as an independent cloud data-loss-prevention (DLP) startup for SaaS applications. Palo Alto Networks acquired it in 2022, and the product now operates as SaaS Security, a module of the company's Prisma SASE platform also referred to as its Next-Gen CASB. The original gamma.ai site now redirects visitors to Palo Alto Networks with a banner confirming the change.
Read More
SaaS Security discovers and categorizes SaaS applications across an organization, including unsanctioned 'shadow IT' tools and generative AI applications such as copilots, plugins, and AI agents. Palo Alto Networks says the discovery engine draws on machine-learning models trained across its customer base, extending visibility beyond individual apps to whole SaaS and AI ecosystems.
Its data protection layer runs multimodal, context-aware data loss prevention across email, SaaS collaboration apps, and GenAI tools, both inline and through API connections. Palo Alto Networks reports this reduces false positives by 95% compared with older approaches. A companion capability, AI Access Security, lets security teams monitor which GenAI apps employees are using and block sensitive data from being uploaded into third-party AI or LLM training pipelines.
The product also runs proactive posture checks: it automatically finds and helps fix misconfigurations, hardens multi-factor authentication settings, and benchmarks security-impacting configurations against industry standards. On the threat side, Palo Alto Networks' Precision AI security services add inline machine-learning malware prevention, Zero Trust blocking of malicious links shared in SaaS chats, and user and entity behavior analytics (UEBA) to flag anomalous activity. All of this is managed from a single console shared with the rest of the Prisma SASE platform.
SaaS Security is built for enterprise IT and security teams managing large numbers of SaaS and GenAI applications, not for individual users or small teams. Palo Alto Networks does not publish public pricing for the module; access is arranged through a sales demo or an existing Prisma SASE account team.
- CategorySecurity & Privacy
- Pricing ModelContact sales
- DeploymentCloud
Palo Alto Networks SaaS Security's Core Features
Automatic discovery of sanctioned and unsanctioned (shadow IT) SaaS applications
Detection of shadow GenAI usage, including AI copilots, plugins, and agents
AI-based, context-aware data loss prevention across SaaS, email, and GenAI apps
AI Access Security for governing and monitoring employee use of generative AI tools
Automatic detection and remediation of SaaS misconfigurations and weak MFA settings
Inline machine-learning malware prevention and Zero Trust threat blocking
User and entity behavior analytics (UEBA) for anomalous SaaS activity
Unified management console shared with the Prisma SASE platform
How to use Palo Alto Networks SaaS Security?
Request access: Contact Palo Alto Networks sales or request a demo of SaaS Security.
Connect SaaS apps: Onboard sanctioned applications through API connectors for discovery and monitoring.
Review discovered apps: Use the automated inventory to review shadow IT and shadow GenAI applications found across the organization.
Configure DLP policies: Set data-loss-prevention and access rules for sensitive data across connected apps.
Monitor and remediate: Track violations, misconfigurations, and threats from the unified console, and apply fixes.
Palo Alto Networks SaaS Security's Use Cases
- Shadow IT discovery
- GenAI data governance
- SaaS DLP
- SaaS posture management