Description
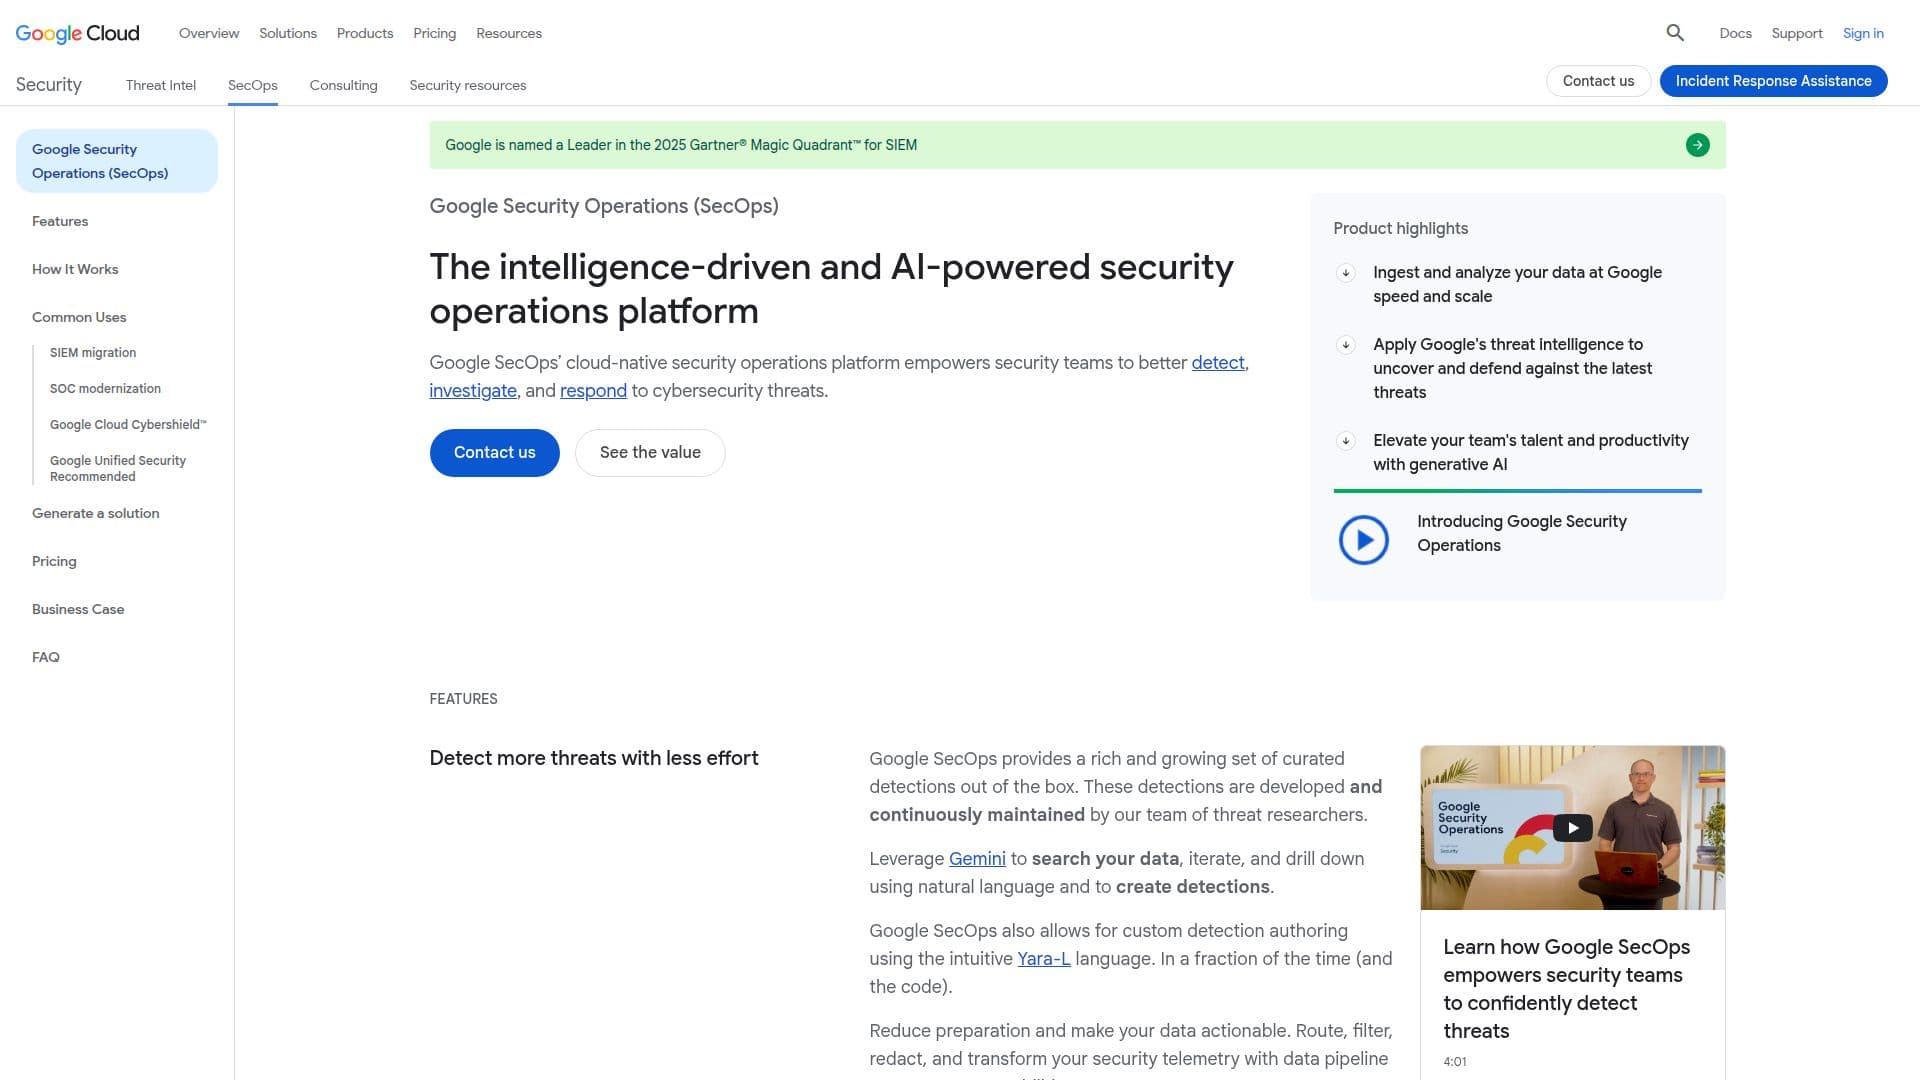
Google Security Operations, previously known as Chronicle, is a comprehensive security platform designed to enhance the capabilities of security teams. It leverages Google's speed, scale, and intelligence to enable teams to detect, investigate, and respond to threats more effectively. The platform offers a unified experience across Security Information and Event Management (SIEM), Security Orchestration, Automation, and Response (SOAR), and threat intelligence, facilitating better detection, investigation, and response.
Read More
The platform allows users to ingest and analyze data at Google speed and scale, applying Google's threat intelligence to uncover and defend against the latest threats. It elevates team productivity with generative AI, enabling faster threat detection with less effort, providing the right context for investigations, and ensuring rapid and precise responses.
Google Security Operations includes various packages based on data ingestion, with one year of security telemetry retention at no additional cost. The Standard package includes core SIEM and SOAR capabilities, supporting up to 1,000 single-event and 75 multi-event rules. The Enterprise package expands support to unlimited environments and includes user and entity behavior analytics (UEBA) capabilities.
The Enterprise Plus package offers advanced features, including a detection engine supporting up to 3,500 single-event rules and 200 multi-event rules, and full access to Google Threat Intelligence, which includes Mandiant and VirusTotal. This package also provides advanced filtering, redaction, transformations, and routing options for data pipeline management.
Google Security Operations is designed for security teams looking to modernize their Security Operations Center (SOC) and improve their cyber defense capabilities. It is suitable for organizations of all sizes, offering scalable solutions to meet diverse security needs. The platform's integration with Google Cloud services ensures seamless operation and enhanced security posture.
- CategoryAI Cybersecurity Tools
- Pricing ModelPackage-based
- DeploymentCloud
- PlatformsWeb
Google Security Operations's Core Features
Unified SIEM and SOAR experience
Google speed and scale data ingestion
Generative AI for enhanced productivity
Threat intelligence application
12-month security telemetry retention
Advanced detection engine
User and entity behavior analytics
Full access to Google Threat Intelligence
How to use Google Security Operations?
Configure: Set up data ingestion and threat detection rules
Use: Monitor threats and conduct investigations
Optimize: Utilize generative AI for enhanced productivity
Respond: Implement automated response actions
Google Security Operations's Use Cases
- Threat Detection
- Security Investigation
- SOC Modernization
- Data Ingestion
- Threat Intelligence