Description
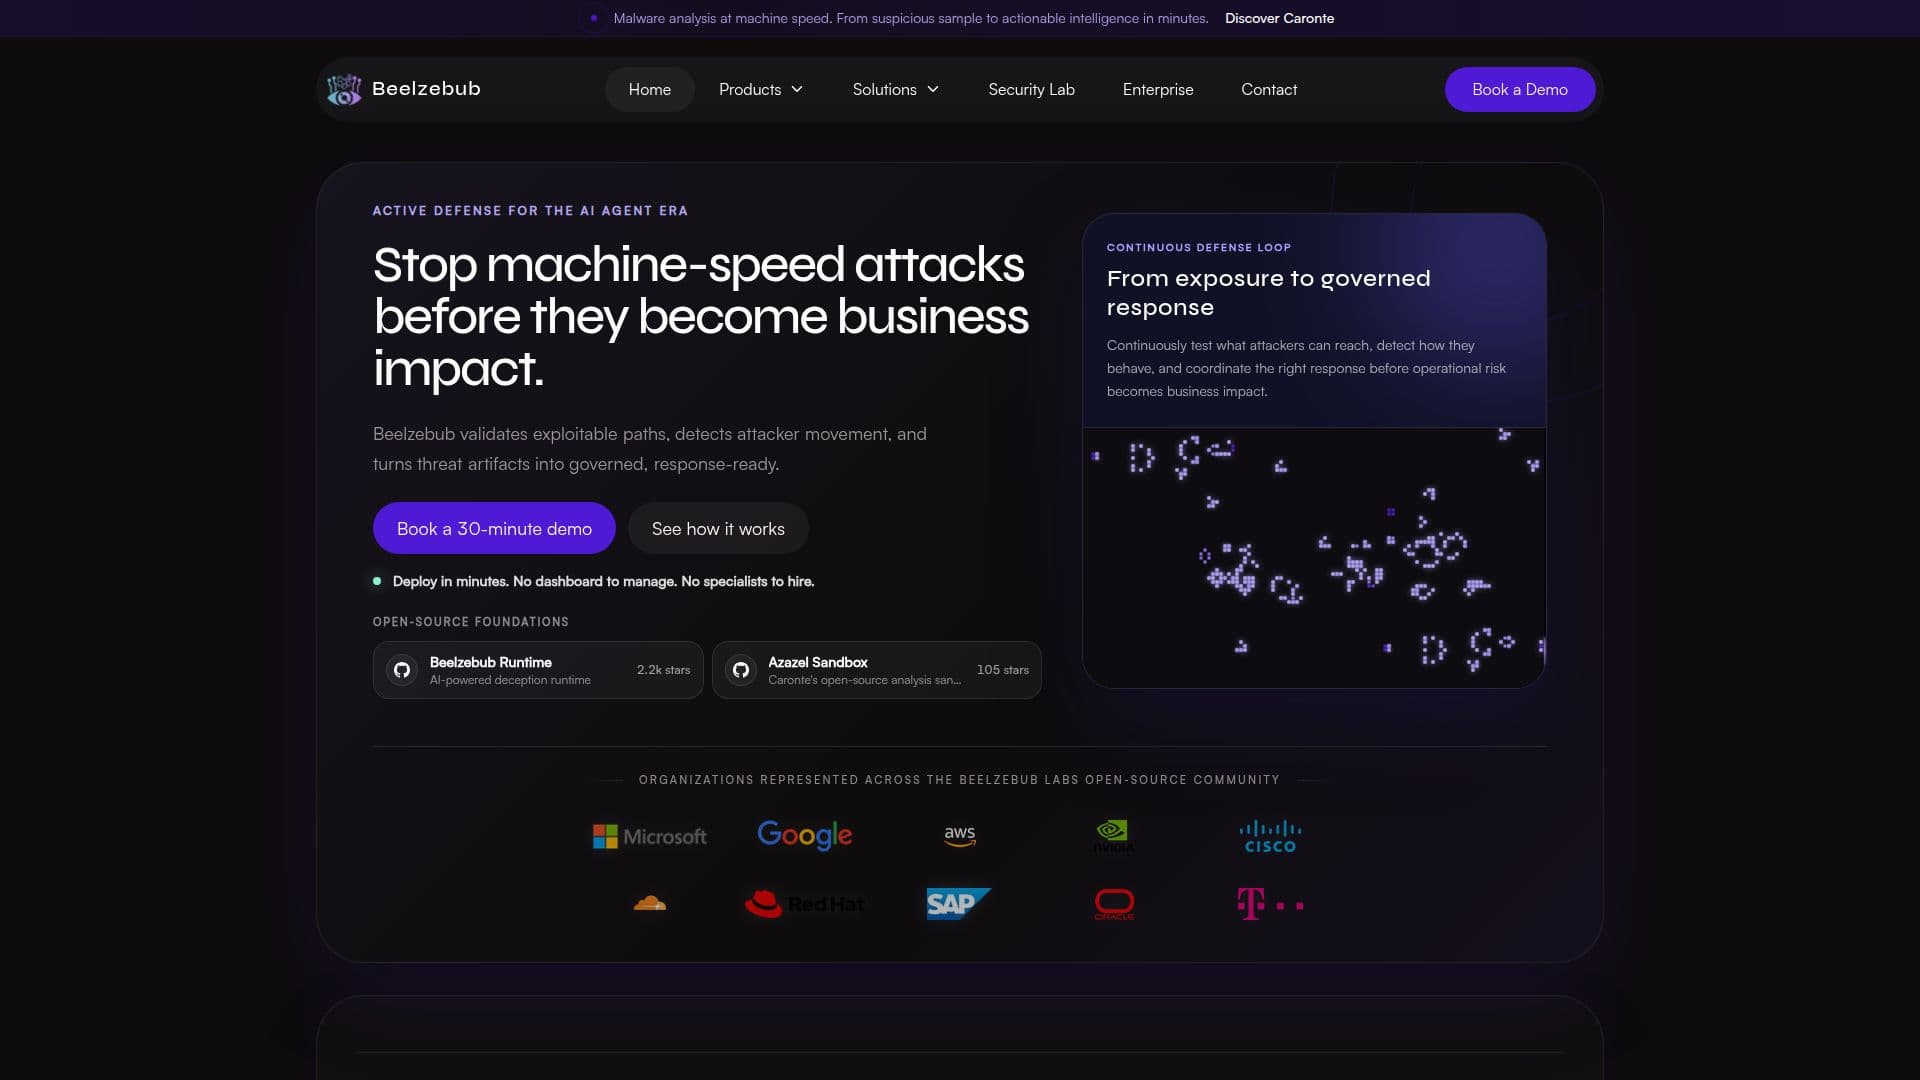
Beelzebub is an AI-native active defense platform that provides organizations with the tools to validate exploitable paths, detect attacker movement, and transform threat artifacts into governed, response-ready evidence. The platform is designed to stop machine-speed attacks before they can impact business operations. Beelzebub operates on open-source foundations and offers a continuous defense loop, allowing organizations to continuously test what attackers can reach, detect how they behave, and coordinate the appropriate response before operational risks become business impacts.
The platform is divided into three main components: Arcangelo, Beelzebub Platform, and Caronte. Arcangelo continuously maps the attack surface and proves which paths are exploitable, combining Internal and External Attack Surface Management with agentic penetration testing. The Beelzebub Platform uses deception to place realistic decoys and canary credentials, providing high-confidence signals for Security Operations Centers (SOC). Caronte turns attacker artifacts into actionable intelligence in minutes, using the open-source Azazel sandbox for isolated behavioral analysis.
Beelzebub is designed for easy deployment, with no dashboard to manage and no specialists required to hire. It supports deployment across cloud and on-premises environments using Docker or Kubernetes. The platform integrates with existing security tools like SIEM, SOAR, and XDR, providing verified context and evidence that security teams can trust.
The platform is particularly useful for SOC and Blue Teams, as well as Cyber Threat Intelligence (CTI) and Incident Response teams. It offers high-confidence alerts based on direct interaction with decoys and provides AI-led investigation, reporting, and response orchestration. Beelzebub's open-source honeypot framework is engineered to create a secure environment for detecting and analyzing cyber threats, supporting multi-protocol decoys like SSH, HTTP, TCP, and MCP to detect prompt injection attacks against LLM agents.
Beelzebub's Core Features
AI-native active defense
Open-source foundations
Continuous defense loop
Deception across cloud, Kubernetes, networks, APIs, and AI agent surfaces
High-confidence alerts
AI-led investigation and response
Easy deployment with Docker and Kubernetes
Integration with SIEM, SOAR, and XDR
How to use Beelzebub?
Deploy: Set up using Docker or Kubernetes
Configure: Place decoys and canary credentials
Monitor: Detect attacker movement and receive alerts
Respond: Use AI-led investigation for response orchestration
Beelzebub's Use Cases
- Attack Surface Management
- Deception Technology
- Incident Response
- Threat Intelligence
- Security Operations